
Don't Copy From This Blog...

Security Master AV is a fake anti-virus program that uses misleading methods to make you think that your computer is infected with malicious software. First, it displays fake security warnings and claims that malicious software has been detected on your computer. Then, it runs a fake system scan and displays a list of infected files. Of course, the scan results are false. Security Master AV flags harmless files as malware. It may also list Windows system files in its scan report, so don't manually delete any of those files. Finally, the rogue program will prompt you to pay for a full version of the program to remove the infections. It goes without saying that you shouldn't purchase it. Instead, please remove Security Master AV from your computer as soon as possible using the removal instructions below.

You may ask, where did it come from? Usually, such bogus programs come from fake online scanners and fake video websites sites or you may simply click an infected advertisement. Security Master AV can come bundled with other malware, but this is less common situation. By the way, the rogue program has to be manually installed, but the problem is that it pretends to be a legitimate program, that's why some users don't understand that it's actually a Trojan or other malware. Once installed, Security Master AV will display fake security alerts. Some of those alerts or pop-ups read:
"System alert
Potentially harmful programs have been detected in your
system and need to be dealt with immediately. Click here to
remove them using Security Master AV."
"System alert
Suspicious software which may be malicious has been detected on your PC. Click here to remove this threat immediately using Security Master AV."

Furthermore, this fake program hijacks Internet Explorer and changes default search engine to findgala.com. It blocks security related websites, modifies Windows Hosts file and blocks legitimate anti-malware programs. Thankfully, we've got remove instructions to help you. It's possible to remove Security Master AV manually, but we strongly recommend you to scan your PC with reputable and legitimate anti-malware software. Please follow the removal instructions below. And by the way, if you have already purchased SecurityMasterAV, then you should contact your credit card company and dispute the charges. Also, if you have any questions or additional information about this virus, please leave a comment. Good luck and be safe!
Security Master AV removal instructions using HijackThis (in Normal mode):
1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro).
Launch the iexplore.exe and click "Do a system scan only" button.
If you can't open iexplore.exe file then download explorer.scr and run it.
2. Search for similar entries in the scan results:
O4 - HKCU\..\Run: [Security Master AV] "C:\Documents and Settings\All Users\Application Data\345d567\SM345d.exe" /s /d
Select all similar entries and click once on the "Fix checked" button. Close HijackThis tool.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
Security Master AV removal instructions (in Safe Mode with Networking):
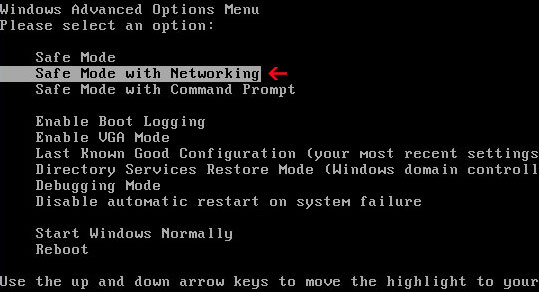
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Security Master AV associated files and registry values:
Files:
You may ask, where did it come from? Usually, such bogus programs come from fake online scanners and fake video websites sites or you may simply click an infected advertisement. Security Master AV can come bundled with other malware, but this is less common situation. By the way, the rogue program has to be manually installed, but the problem is that it pretends to be a legitimate program, that's why some users don't understand that it's actually a Trojan or other malware. Once installed, Security Master AV will display fake security alerts. Some of those alerts or pop-ups read:
"System alert
Potentially harmful programs have been detected in your
system and need to be dealt with immediately. Click here to
remove them using Security Master AV."
"System alert
Suspicious software which may be malicious has been detected on your PC. Click here to remove this threat immediately using Security Master AV."
Furthermore, this fake program hijacks Internet Explorer and changes default search engine to findgala.com. It blocks security related websites, modifies Windows Hosts file and blocks legitimate anti-malware programs. Thankfully, we've got remove instructions to help you. It's possible to remove Security Master AV manually, but we strongly recommend you to scan your PC with reputable and legitimate anti-malware software. Please follow the removal instructions below. And by the way, if you have already purchased SecurityMasterAV, then you should contact your credit card company and dispute the charges. Also, if you have any questions or additional information about this virus, please leave a comment. Good luck and be safe!
Security Master AV removal instructions using HijackThis (in Normal mode):
1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro).
Launch the iexplore.exe and click "Do a system scan only" button.
If you can't open iexplore.exe file then download explorer.scr and run it.
2. Search for similar entries in the scan results:
O4 - HKCU\..\Run: [Security Master AV] "C:\Documents and Settings\All Users\Application Data\345d567\SM345d.exe" /s /d
Select all similar entries and click once on the "Fix checked" button. Close HijackThis tool.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
Security Master AV removal instructions (in Safe Mode with Networking):
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Security Master AV associated files and registry values:
Files:
- C:\Documents and Settings\All Users\Application Data\345d567\
- C:\Documents and Settings\All Users\Application Data\345d567\16.mof
- C:\Documents and Settings\All Users\Application Data\345d567\mozcrt19.dll
- C:\Documents and Settings\All Users\Application Data\345d567\SM345d.exe
- C:\Documents and Settings\All Users\Application Data\345d567\SMAV.ico
- C:\Documents and Settings\All Users\Application Data\345d567\sqlite3.dll
- C:\Documents and Settings\All Users\Application Data\345d567\Quarantine Items\
- C:\Documents and Settings\All Users\Application Data\345d567\SMAVSys\
- C:\Documents and Settings\All Users\Application Data\345d567\SMAVSys\vd952342.bd
- C:\Documents and Settings\All Users\Application Data\SMNPCTCAV\
- %UserProfile%\Start Menu\Security Master AV.lnk
- %UserProfile%\Start Menu\Programs\Security Master AV.lnk
- HKEY_CURRENT_USER\Software\3
- HKEY_CLASSES_ROOT\CLSID\{3F2BBC05-40DF-11D2-9455-00104BC936FF}
- HKEY_CLASSES_ROOT\SM345d.DocHostUIHandler
- HKEY_USERS\.DEFAULT\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=7&q={searchTerms}"
- HKEY_CURRENT_USER\Software\Classes\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=7&q={searchTerms}"
- HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "RunInvalidSignatures" = "1"
- HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "Security Master AV"
- HKEY_CLASSES_ROOT\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=7&q={searchTerms}"
- HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "CheckExeSignatures" = "no"


