Friday, June 14, 2013

Remove TR/ATRAPS.Gen2, removal instructions

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Cyber crooks and third parties that buy stolen data are increasingly using more and more sophisticated techniques, in a variety of different ways to steal your information for financial gain or to simply cause havoc on your computer seemingly for their own twisted sense of enjoyment. One of these dangers to look out for is called TR/ATRAPS.Gen2 which is a piece of malicious software in disguise. This Trojan is a tough one to remove because most of the time it comes bundled with TR/Sirefef which is a rather sophisticated malware from the Sirefef or ZeroAccess malware family. So, if you are getting a pop-up from your antivirus about this infection then your current security product is unable to remove it properly.

As far as I can tell, TR/ATRAPS.Gen2 is distributed in various ways, using infected websites, malicious emails and even game cracks or free premium account generators. Just because a program says it’s a game and it looks like a game, it is not necessarily a game and it might actually be a Trojan horse. In fact some types of Trojan horse software are programs that masquerade as anti-virus software - although they’re actually infecting you with viruses and are the very thing they claim to be protecting you against! Learn more: Rogue Antivirus software.

Access to file containing the virus or unwanted program 'TR/ATRAPS.Gen2' was blocked. 

As with types of viruses and malware, not all Trojan horses are the same either and they are split into categories depending on how they access your computer’s system and the type of damage they cause. TR/ATRAPS.Gen2 may be used to steal sensitive information, display ads on your computer or redirect your web browser to infected websites. It can also download additional malware modules onto your computer. As you can see, this Trojan horse is really well designed and coded. Detection ratio speaks for itself, it's usually below 50%, see this. I've seen some fresh samples that were detected by only two or three antivirus programs which means, this malware uses advanced techniques to bypass antivirus protection.

Unfortunately for computer users, whether it’s just you at home alone on your laptop or a network administrator in a busy corporate environment, attacks by Trojan Horses are increasing not only in amount but in sophistication too. They affect users in all countries across the globe and no one is immune so how do you protect yourself from falling victim?

The thing to remember is that just as the people of Troy were fooled by the Greeks into letting them into their city to capture it, computer Trojan horses operate on the same principle. An attacker will try to convince you to run TR/ATRAPS.Gen2 on your computer by making you think it’s perfectly safe. It is for this reason that most Trojan Horses are hidden inside games or other popular downloads.

Luckily a good (genuine!) anti-malware program will detect and delete the TR/ATRAPS.Gen2 virus before you have a chance to run them, thus installing them on your PC. It goes without saying, therefore, that you should always have decent anti-malware software installed and you should also make sure it is the most up to date version.

You should also take care not to do as the Trojans did and let ‘the horse’ in. This means never clicking on an email attachment from a sender you do not know and not downloading or installing games, anti-viruses or other programs from sources that you do not trust or are unsure about. To remove TR/ATRAPS.Gen2 from your computer, please follow the removal instructions below. If you have any questions, please leave a comment below. Good luck and be safe online!

Written by Michael Kaur, http://spywareremovalx.blogspot.com


TR/ATRAPS.Gen2 removal instructions:

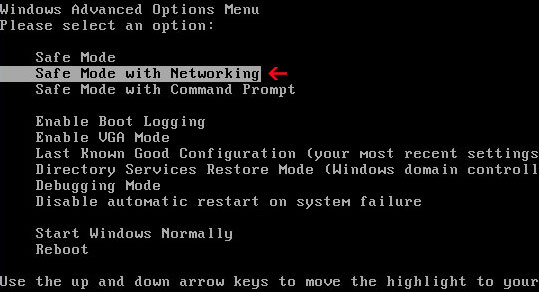
1. Please reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key.

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download recommended anti-malware software (direct download) and run a full system scan to remove TR/ATRAPS.Gen2 from your computer.

3. Reboot your computer as normal. Download and run TDSSKiller. Press the button Start scan for the utility to start scanning.


4. Wait for the scan and disinfection process to be over. Then click Continue. Please reboot your computer after the disinfection is over.


Thursday, June 13, 2013

How to remove 'TidyNetwork' adware virus from your computer

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
As internet users most of us have seen those irritating little pop-up windows that are advertising something that we normally have little or no interest in, but what are they, why do they suddenly appear and how can you get them to go away? Read on as this article takes a look at the adware called "TidyNetwork".

This adware is usually encountered as as a media player, fake Flash Player update or simply a plug-in required for viewing contents on some maliciously crafted websites. It may also come bundled with other applications, usually freeware, for instance codec packs and fake Java updates. You may also have heard the term spyware used when talking about adware and this is something that is often bundled in with adware. Spyware is a type of monitoring software which is installed on your computer alongside the adware. It constantly tracks your internet usage and reports back to the owner of the program, telling them what websites you are visiting. This enables them to target you with more relevant adverts thus increasing the likelihood of you clicking on the ad and spending money. For example, if you are looking for information about payday loans, you will quickly notice that certain keywords in pretty much every website you visit get underlined and hovering over them shows a popup from TidyNetwork. Even if it's Wikipedia, Yahoo News or your local community website. This adware can inject ads on any website if only it finds suitable keywords for advertisements.

Advertising companies normally have privacy policies stating that they will not collect personal information or data that enables you to be identified however, regardless of this, the fact is that you still have a live application on your computer that is logging your internet usage habits and is relaying information about you to a remotely located third party. This is way some antimalware programs detect it as a Trojan, malware or PUP.Tidynetwork. Something that shouldn't be there and needs your attention.

So if you are seeing pop-up adverts from Tidy Network on your PC does that mean that you are also being spied upon? Not necessarily; not all adware comes with spyware, some of them really are just adverts, but in actual fact, the majority of them are not and they do have spyware packaged with them. I'm saying this because, this adware is not the same for everyone.

So, if you have any concerns about your online privacy it stands to reason that you may not be entirely comfortable with having adware - and spyware - on your computer system. It is not a particularly pleasant feeling to know that data concerning the websites you visit is being logged and transmitted to someone, particularly as it is doing so via your own internet connection!

A genuine adware company should state exactly what data is being recorded and sent in a privacy policy statement however for the regular home computer user there is virtually no way for them to control what information is being transmitted. As technology gets cleverer by the day, theoretically speaking the server that is collecting the data on you could be logging a lot more info than just which websites you are visiting which is why it is wise to protect yourself from adware TidyNetwork, and in particular spyware.

The best defense against having your privacy violated? Protect yourself, your data and your identity by installing reputable anti-malware program on your computer - today! If you don't know how to get rid of TidyNetwork adware or you suspect that it might still lurk on your computer, please follow the removal guide below. If you have any questions, please leave a comment below. Good luck and be safe online!

Written by Michael Kaur, http://spywareremovalx.blogspot.com


TidyNetwork removal instructions:

1. First of all, download recommended anti-malware software and run a full system scan. It will detect and remove this infection from your computer. You may then follow the manual removal instructions below to remove the leftover traces of this infection. Hopefully you won't have to do that.


2. Remove TidyNetwork.com application from your computer using the Add/Remove Programs control panel (Windows XP) or Uninstall a program control panel (Windows 7 and Windows 8).

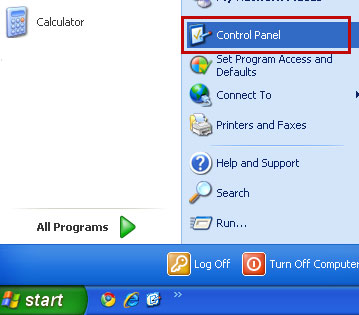
Go to the Start Menu. Select Control Panel → Add/Remove Programs.
If you are using Windows Vista or Windows 7, select Control Panel → Uninstall a Program.


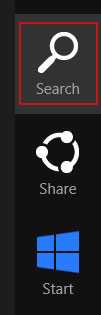
If you are using Windows 8, simply drag your mouse pointer to the right edge of the screen, select Search from the list and search for "control panel".


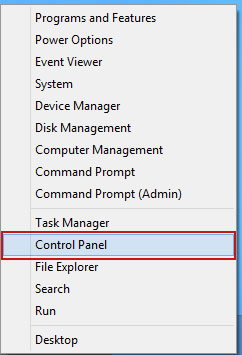
Or you can right-click on a bottom left hot corner (formerly known as the Start button) and select Control panel from there.


3. When the Add/Remove Programs or the Uninstall a Program screen is displayed, scroll through the list of currently installed programs and remove the following TidyNetwork.com.


If you are using Windows Vista, Windows 7 or Windows 8, click Uninstall up near the top of that window. When you're done, please close the Control Panel screen.


Remove TidyNetwork ads from Google Chrome:

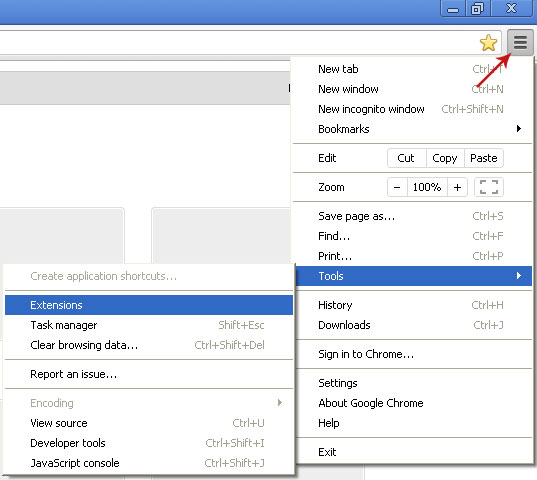
1. Click on Chrome menu button. Go to Tools → Extensions.


2. Click on the trashcan icon to remove the TidyNetwork.com extension:


Remove TidyNetwork ads from Mozilla Firefox:

1. Open Mozilla Firefox. Go to Tools → Add-ons.


2. Select Extensions. Click Remove button to the TidyNetwork 4.0 extension.


Remove TidyNetwork ads from Internet Explorer:

1. Open Internet Explorer. Go to Tools → Manage Add-ons. If you have the latest version, simply click on the Settings button.


2. Select Toolbars and Extensions. Click Remove/Disable button to remove the TidyNetwork browser add-on.

Wednesday, June 12, 2013

What is stij.exe and how to remove it?

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection

stij.exe - IBUpdaterService by Perion Network Ltd.


What is stij.exe?


stij.exe is digitally signed by Perion Network Ltd. which means that you probably installed one of their products, for instance MyStart by Incredibar or Incredimail. Even if you didn't, it might have come bundled with adware that drops this file on your computer during the installation process. Later this file may be used to download and install additional adware/spyware onto your computer without your knowledge and permission. The file runs automatically every time Windows starts. It even creates a separate Windows service. Needless to say, it's not essential for Windows and may cause problems. Not to mention annoying and intrusive ads. stij.exe may also cause your computer to lag out. Some antivirus products detect this application as InstallBrain adware, PUP.InstallBrain others simply flag it as generic Trojan horse. I recommend you to remove stij.exe from your computer.


Security Rating: Potentially Dangerous

File name: stij.exe
Publisher: Perion Network Ltd.
File Location Windows XP: C:\Windows\System32\jmdp\stij.exe
File Location Windows 7: C:\Windows\SysWOW64\jmdp\stij.exe
Startup file: SYSTEM\CurrentControlSet\Services 'IBUpdaterService' (Updater Service)

What is wscript.exe and how to remove it?

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection

wscript.exe - Windows-based script host by Microsoft


What is wscript.exe?


wscript.exe is a Windows service that allows you to execute VBScript files. Normally, it is not dangerous, but if a malicious script is downloaded and executed it will appear as if wscript.exe is the culprit, when it is really a separate .vbs file. Antivirus programs usually detect C:\Windows\System32\wscript.exe as the culprit, however, it's not necessarily infected. It may be that your computer is infected with Worms and Trojans that attempt to execute malicious .vbs scripts. Most users, get these malware infections from SD cards, pen drives and of course infected websites. Malicious files may change Windows registry, establish connection to remove servers controlled by cyber crooks and download additional malware modules. Other issues: can't open Regedit, certain Windows options are missing, can't acces Contol Panel. Malware may also block anti-malware and Windows system utilities. You should not delete wscript.exe manually, many Windows services require it and our computer may not function properly if it cannot be found. But you should use recommend anti-malware software to remove wscript.exe related malware from your computer.


Security Rating: Potentially Dangerous

File name: wscript.exe
Publisher: Microsoft
File Location Windows XP: C:\Windows\System32\wscript.exe
File Location Windows 7: C:\Windows\System32\wscript.exe
Startup file: SYSTEM\CurrentControlSet\Services 'Windows-based script host'

How to remove Luhe.Sirefef.A Trojan virus (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Luhe.Sirefef.A is a malicious Trojan horse from the Sirefef malware family. Just as the good people of Troy unwittingly let their enemies into their midst, this Trojan horse will similarly trick you into infecting your own computer and being the catalyst for the damage that will then occur. How this happens is that the person who wrote and coded the Trojan horse manipulates you by convincing you to either perform an action or offer personal information, either without you realising you’re doing it, or against your better judgement. The threat is currently spreading and is ranked 60 in the world for online threats, according to AVG. Which means that there are at least 100K infected computers. If you received a pop-up warning "Found Luhe.Sirefef.A" paired with other Trojans, for example, Trojan horse Generic32.CEMU, then your computer is definitely infected with this rather sophisticated malware. Sometimes, antivirus programs cannot properly remove this infection. Most of them will suggest you to remove Luhe.Sirefef.A manually, however, this can be really difficult task. First of all, because it's a deeply embedded virus. Secondly, you can be 100% that your computer is clean, even if you think that you removed all the malicious files. So, to remove this Trojan from your computer, please follow the removal guide below.


Cyber crooks distribute this Trojan in every possible way to reach as many PC users as possible. Usually, they use hacked websites. They may also send you an email with an infected attachment, which once clicked upon will run the Trojan horse and infect your PC or laptop. For example let’s say the email has a game attached to it – it looks great fun and you can’t wait to get playing. So what do you do? You run the .exe file in order to install the game on your computer but bingo – you’ve just installed the Luhe.Sirefef.A Trojan.

What the Trojan horse will then do is to start over-writing certain sections of your hard drive thus corrupting your files and data. Very often, this virus is detected in services.exe and other system files. The only small silver lining to this cloud is that Trojan horses are not actually viruses (although many people tend to think of them as such). A computer virus will replicate itself but a Trojan horse will not. The good thing about this is that Trojan horses only wreak their damage if they are given the opportunity to run and the majority of good anti-malware software will be able to detect and delete Trojan horse software before you have a chance to do anything with it.

So what is the moral of this story that started off with a Greek army and ended up with data corruption? The number one rule is the same that should be applied when protecting yourself from all forms of malicious software and viruses: make sure you have a well-known brand of anti-malware software installed on your computer to stop Luhe.Sirefef.A in its track. And make sure it’s the latest version too.

Furthermore, don’t open programs or download software unless you are 100% sure that they come from a reliable and trusted source – particularly if they have been sent to you in the form of an executable file attached to an email. And if you don’t know the sender; then definitely don’t touch it. Remember that this is exactly the way Trojan horses work – don’t make the same mistake as the people of Troy did by letting it through the ‘gates’ of your computer. If you antivirus was unable to disinfect Luhe.Sirefef.A, please follow the removal instructions below on how to eliminate this and any other threat from your computer. If you have any questions, please leave a comment below. Good luck and be safe online!

Written by Michael Kaur, http://spywareremovalx.blogspot.com


Luhe.Sirefef.A removal instructions:

1. Please reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key.


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download recommended anti-malware software (direct download) and run a full system scan to remove this Trojan from your computer.

3. Reboot your computer as normal. Download and run TDSSKiller. Press the button Start scan for the utility to start scanning.


4. Wait for the scan and disinfection process to be over. Then click Continue. Please reboot your computer after the disinfection is over.


 
//PART 2