Monday, June 10, 2013

What is minerd.exe and how to remove it?

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection

minerd.exe - CPU miner for Bitcoin


What is minerd.exe?


minerd.exe is a part of multi-threaded CPU miner for Bitcoin crypto-currency system. Very often this application causes CPU usage to go to 90% or even more. Needles to say it's not essential for Windows and may cause problems. If you knowingly installed this Bitcoin miner on your computer then there's nothing to worry about. Even if you antivirus says it's a trojan horse it's probably a false positive. However, cyber crooks and fraudsters are using this software to earn some extra money as well by monetizing botnets. They drop the main mining modules on infected computers and start mining. They usually set low mining speed, so that the minerd.exe process only uses unused CPU cycles. But others don't. Infected users quickly notice that their computers became very slow. This is a sign that your computer is infected and not only with RiskTool.Win32.BitCoinMiner or PUP.BitCoinMiner but also with Trojan downloaders and spyware. I recommend you to remove minerd.exe from your computer.


Security Rating: Potentially Dangerous

File name: minerd.exe
Publisher: Litecoin
File Location Windows XP: %APPDATA%\pooler-cpuminer\minerd.exe
File Location Windows 7: %APPDATA%\pooler-cpuminer\minerd.exe
Startup file: HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run 'minerd.exe'

What is wssetup.exe and how to remove it?

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection

wssetup.exe by Perion Network LTD


What is wssetup.exe?


wssetup.exe is the software installation package by Perion Network Ltd. It may install SweetIM, MyStart by Incredibar, Incredimail and a few other applications. It may be bundled with third-party applications as well. This application is not essential for Windows and may cause problems. You may get a Windows message that asks if you want to allow the file WSSetup.exe by Perion Network LTD to install every time you power up or restart your computer. The file is usually loaded from the TEMP folder which means that one of Perion products is already installed on your computer and wants to install additional software or some other applications dropped the installation package on your computer. Since most of the time Perion products come bundled with adware (AdWare.Win32.Gator by Kaspersky) or spyware I recommend you to remove wssetup.exe from your computer.


Security Rating: Potentially Dangerous

File name: wssetup.exe
Publisher: Perion Network Ltd.
File Location Windows XP: C:\Documents and Settings\[UserName]\Local Settings\Temp\[random]\wssetup.exe
File Location Windows 7: C:\Users\[UserName]\AppData\Local\temp\[random]\wssetup.exe
Startup file: %TEMP%

Saturday, June 8, 2013

Alert: Fake Google Chrome Update

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
A fake Google Chrome update warning pop-up page has appeared in my browser today. The fake update looks similar to the following:


Please Update to the Latest Version of Chrome


URGENT!
Your version of Chrome 27 may be outdated and could be vulnerable to attacks.

This isn't the first time when scammers push websites offering PUPs and adware for instance WebCake, as updates to Google's Chrome browser. By the way they use pretty much the same fake Firefox update page to scare Firefox users and to lure them into installing adware. Please be aware this is NOT an actual update. It could be that you just accidentally visited a shady website and got this fake update warning but if it keeps popping up like five minutes or so, then your computer is probably infected with adware or potentially unwanted software. How do you know if your PC is infected?
  • Have annoying pop-up adverts suddenly started appearing and interrupting you whenever you’re online?
  • Are you seeing a strange tool bar on your internet browser that wasn’t there previously and that you did not download or install yourself?
  • Has your computer suddenly become sluggish and started running a lot more slowly than it usually does? Is it still running slowly even after you’ve deleted unnecessary files, downloads and programs and freed up hard disk drive space or taken other maintainance actions?
  • Are you having problems accessing your anti-virus or other security software?
  • Do your computer’s settings seem to have changed without you doing anything?
  • Are there strange websites or pages saved in your ‘Favorites’ folder or bookmarked websites list?
If you’ve answered yes to one or more of the above don’t worry, you’re not going mad – but you probably have had your browser hijacked by an unscrupulous attacker. If you have encountered this update and clicked on the links it provided, please scan your computer recommend anti-malware software.


If you have any questions, please leave a comment below. Good luck and be safe online!

Fixing ievbz.com redirection/hijacking problem

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
In this article we’re going to take a look at ievbz.com redirection problem and find out how you can tell if your browser has been hijacked, how it will affect your computer and what you can do to prevent yourself from becoming a victim.

If you are occasionally redirected to a site that has the suffix ievbz.com then your web browser has been hijacked. Browser hijacking is a type of internet fraud. It’s another unwelcome addition to the long list of cyber scams along with Trojan horses, spyware, malware, worms, fake anti-virus software and police themed ransomware. Browser hijacking is just as the name suggests – it means someone has taken over your internet browser without your permission or knowledge. Put simply it is cyber kidnapping. Unlike a regular virus, however, a hijacker will be able to access your browser through a program that you yourself have intentionally installed on your PC. In most cases you will be completely unaware that the program you’ve downloaded – be it a game, a software update or even an anti-virus program – has been bundled with a hijacking program and even some of the most reputable programs can come with a piece of hijacking software attached.


There are a number of ways to tell if you’ve fallen victim to a browser hijacker so stay vigilant and if you experience any of the following you might need to take further action to rid yourself of the hijacker. In this case, when clicking on links and instead of going to the right site, it will adding ievbz. For example, if you Google something and click on a link, you will be redirected to google.ievbz.com.

In some cases a browser hijacker will have taken control of your browser with the intention of directing you to websites that you may not particularly want to go to. These sites maybe as something as innocent as an online clothing store – or it could be a site containing explicit adult content of a very graphic nature. Whichever it is, basically the hijacker is manipulating you into visiting a site you probably would not have visited. As you can see, at the time I was investigating this malware it redirected me to fake surveys.

As mentioned above hijacking programs can be bundled with something you are downloading and installing but some are also attached to plug-ins that you’ve added to your browser – most commonly toolbars plus other freeware, for instance DownloadTerms which was the culprit of ievbz.com redirection problem.

As usual, prevention is better than cure and browser hijackers can be a pain to remove so take as many steps as possible to prevent it from happening in the first place. Most importantly make sure you have up to date, reputable anti-virus and anti-malware programs installed. Make sure they are enabled and run regularly. Anti-virus and anti-malware programs can differ and they cover different aspects of security so it makes sense to have more than just your standard anti-virus software installed. Block pop-ups from displaying. Whether you use Internet Explorer, Chrome or Firefox you’ll be able to change your PC settings. You will then be notified if a website wants you to enable pop-ups and you can choose to do so only if you trust the site. Check your add-ons and plug-ins and delete any that you’re not using or are not essential.

Written by Michael Kaur, http://spywareremovalx.blogspot.com


ievbz.com removal instructions:

1. First of all, download recommended anti-malware software and run a full system scan. It will detect and remove this infection from your computer. You may then follow the manual removal instructions below to remove the leftover traces of this infection. Hopefully you won't have to do that.


2. Remove ievbz.com related prograsm from your computer using the Add/Remove Programs control panel (Windows XP) or Uninstall a program control panel (Windows 7 and Windows 8).

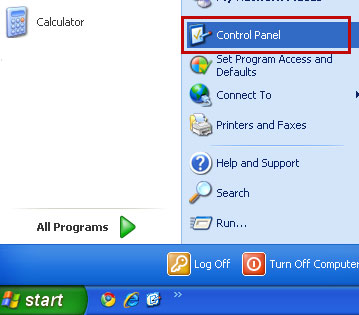
Go to the Start Menu. Select Control Panel → Add/Remove Programs.
If you are using Windows Vista or Windows 7, select Control Panel → Uninstall a Program.


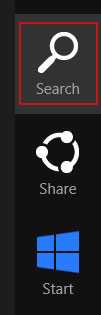
If you are using Windows 8, simply drag your mouse pointer to the right edge of the screen, select Search from the list and search for "control panel".


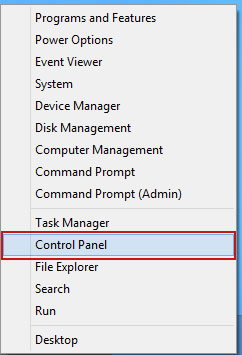
Or you can right-click on a bottom left hot corner (formerly known as the Start button) and select Control panel from there.


3. When the Add/Remove Programs or the Uninstall a Program screen is displayed, scroll through the list of currently installed programs and remove the following:
  • DefaultTab
  • DownloadTerms
  • LessTabs
  • TidyNetwork.com
  • WebCake
  • and any other recently installed application
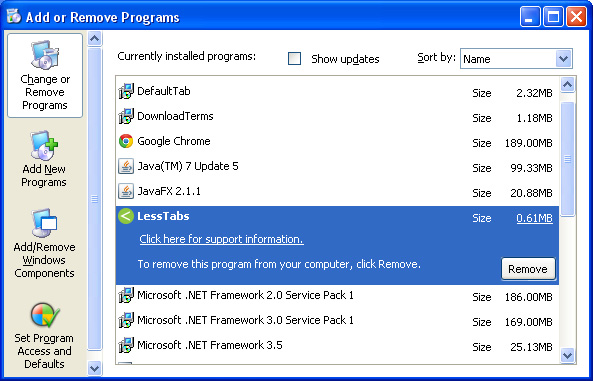

Simply select each application and click Remove. If you are using Windows Vista, Windows 7 or Windows 8, click Uninstall up near the top of that window. When you're done, please close the Control Panel screen.


Remove ievbz.com from Google Chrome:

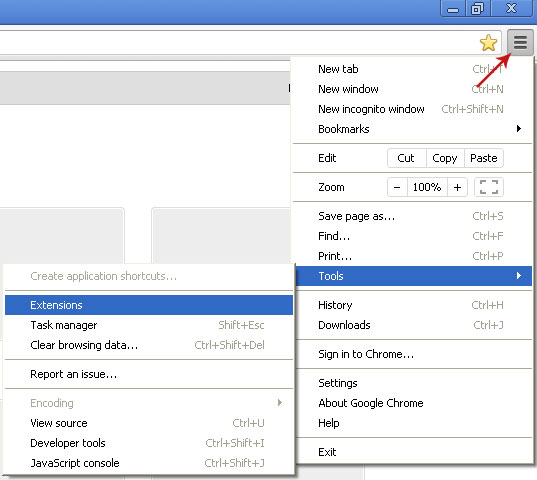
1. Click on Chrome menu button. Go to Tools → Extensions.


2. Click on the trashcan icon to remove the following extensions:


Remove ievbz.com from Mozilla Firefox:

1. Open Mozilla Firefox. Go to Tools → Add-ons.


2. Select Extensions. Click Remove button to the following extensions. If you can't find the Remove button, then simply click on the Disable button.


Remove ievbz.com from Internet Explorer:

1. Open Internet Explorer. Go to Tools → Manage Add-ons. If you have the latest version, simply click on the Settings button.


2. Select Toolbars and Extensions. Click Remove/Disable button to remove the browser add-ons listed above.

What is dmwu.exe and how to remove it?

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection

dmwu.exe - IBUpdaterService by Perion Network Ltd.


What is Dmwu.exe?


dmwu.exe is a part of the Web Optimizer adware that may display advertisements on your computer. This applications may be also installed along with MyStart by Incredibar browser hijacker and other Perion products. It's not essential for Windows and may cause problems, for example you met get a Windows message that dmwu.exe has encountered a problem and similar error pop-ups. Since this application periodically checks for updates it creates a Windows service named IBUpdaterService (Updater Service). Needles to say it runs automatically every time you start your computer. Some users say it slows their machines and even causes system errors. Furthermore, it may download and install additional adware/spyware onto your computer without your knowledge. Some antivirus products detect this application as InstallBrain adware, others simply flag it as generic Trojan horse. I recommend you to remove dmwu.exe from your computer.


Security Rating: Potentially Dangerous

File name: dmwu.exe
Publisher: Perion Network Ltd.
File Location Windows XP: C:\WINDOWS\system32\dmwu.exe
File Location Windows 7: C:\WINDOWS\system32\dmwu.exe
Startup file: SYSTEM\CurrentControlSet\Services 'IBUpdaterService' (Updater Service)

 
//PART 2