Friday, August 31, 2012

Remove search.sweetim.com and SweetIM toolbar (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
I'm sure that you've been frustrated when you installed certain application (mostly freeware or shareware) only to find that it drops additional toolbars and changes your default search engine provider. Rajesh Moganti who authors Geeks Desk Technology Blog has shared some interesting thoughts about SweetIM toolbar and on-going concern regarding web browser modifications.


Important note: SweetIM toolbar and associated components are safe and contain no malicious or dangerous software whatsoever. We know that software developers take this kind of publications very seriously claiming that we are slandering their good reputation. However, that's not true. Even thought, this site deals with malware, we DO NOT refer to the SweetIM as a malicious product. This post provides detailed instructions regarding the way the SweetIM products, including SweetIM toolbar, search.sweetim.com and home.sweetim.com, can be removed by end users. Why? Because you guys made it so freaking confusing that most users don't even know where to start and how to remove all the components of SweetIM products. We know that our readers are smart enough to tell the difference between a potentially unwanted web toolbar and malicious application. Don't worry about that.

SweetIM toolbar is all about fun. SweetPacks team provides a high quality product with loads of fun making features. That's probably the reason why more than 150 million users are using this toolbar across the globe.
  • Animated Smileys. SweetIM toolbar gives you an exclusive free list of animated smileys. These smileys can be sent through different instant messengers, Facebook, email etc. Use of smileys reflects your mood while chatting, sometimes chatting could be boring but this boredom can be wiped out with the use of cute and funky smileys to bring freshness in chatting.

  • Online Games. You can select any of the cool and fun games listed in the toolbar or website and enjoy your time at its fullest. You can invite your friends also to participate for multi-player games.

  • Snick Peak. Before sharing the animation, emoticon, smiley, etc., you can preview it and choose the best one before actually sending it.

  • Search bar. SweetIM toolbar comes with default search bar and search engine provider. Some people find it useful; however, some say it's a nightmare mostly because SweetIM toolbar changes the way people search displaying entirely different search results.

  • SweetIM default Home Page. During the installation, SweetIM asks whether you want to set home.sweetim.com as your default home page and search.sweetim.com as your default web search provider. This is true when you run the official SweetIM installer. However, quite the opposite happens when the toolbar comes bundled with other software, for example freeware players, codes and screens savers.
But not everything about this product is great, especially when it comes to removing the default search engine provider called SweetIM Search which redirects users to search.sweetim.com instead of Google when searching directly from the address bar in Mozilla Firefox, Google Chrome and Internet Explorer. Of course, there's an official removal guide that covers most frequently asked questions but for some odd reasons SweetIM authors forgot to mention that certain web browser settings can be restored manually only. For instance, you have to change default search engine provider and keyword.URL key date value in Mozilla Firefox manually yourself. Why's that? We bet you know that most user do not want to deal with advanced web browser settings. Some of them don't know how to do that in the first place. And that’s not their fault. Such remnants are very annoying, users cannot surf the web as they used to before installing SweetIM. Forcing users to use your web search engine in such unethical manner won't add credibility to your products. It might increase revenue but not the reputation.

To remove search.sweetim.com and SweetIM toolbar from your computer, please follow the removal instructions below. If you have any questions or valuable remarks, please leave a comment below. Good luck and be safe online!

Source: http://spywareremovalx.blogspot.com


Search.sweetim.com and and SweetIM toolbar removal instructions:

1. First of all, download recommended anti-malware software and run a full system scan. It will detect and remove this infection from your computer. You may then follow the manual removal instructions below to remove the leftover traces of this browser hijacker. Hopefully you won't have to do that.


2. Go to the Start Menu. Select Control Panel → Add/Remove Programs.
If you are using Windows Vista or Windows 7, select Control Panel → Uninstall a Program.
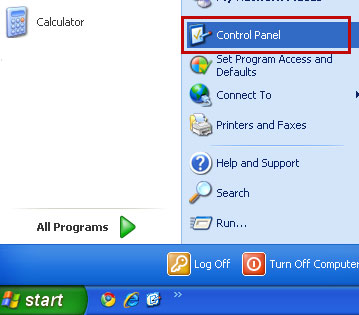


3. Search for SweetIM for Messenger, SweetPacks Toolbar for Internet Explorer and Update Manager for SweetPacks in the list. Select the program and click Remove button. Remove all components!

If you are using Windows Vista/7, click Uninstall up near the top of that window.


Remove search.sweetim.com in Internet Explorer:

1. Go to Tools → Internet Options. Select General tab and click Use default button or enter your own website, e.g. google.com instead of http://home.sweetim.com. Click OK to save the changes.


If your search results are being redirected to search.sweetim.com, please go to Tools → Manage Add-ons and select Search Providers. Choose Bing or Live Search as your default search engine provider and then remove SweetIM Search. Usually, SweetIM Search engine is removed with the core components of SweetIM toolbar in Internet Explorer.


Remove search.sweetim.com and SweetIM toolbar in Mozilla Firefox:

1. Open Mozilla Firefox. Go to Tools → Add-ons.


2. Select Extensions. Remove SweetPacks Toolbar for Firefox toolbar. Close the window.


3. Click on the magnifying glass search icon as shown in the image below and select Manage Search Engines....


4. Choose SweetIM Search from the list and click Remove to remove it. Click OK to save changes.


5. Go to Tools → Options. Under the General tab reset the startup homepage or change it to google.com, etc.


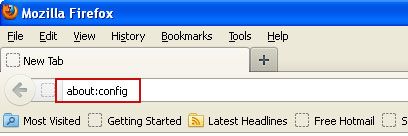
6. In the URL address bar, type about:config and hit Enter.


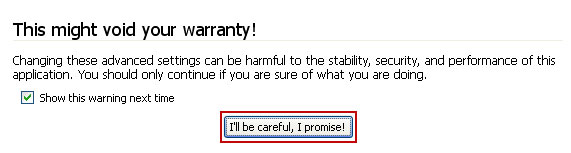
Click I'll be careful, I promise! to continue.


In the filter at the top, type: sweetim


Now, you should see all the preferences that were changed by SweetIM toolbar. Right-click on the preference and select Reset to restore default value. Reset all found preferences!


That's it!


Remove search.sweetim.com and SweetIM for Facebook in Google Chrome:

1. Click on Customize and control Google Chrome icon. Go to Tools → Extensions.
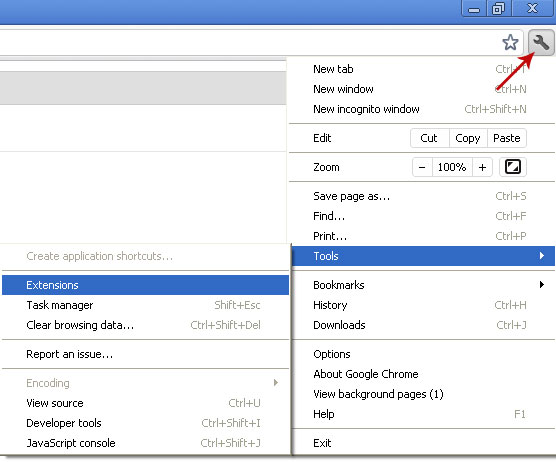


2. Select SweetIM for Facebook and click on the small recycle bin icon to remove the toolbar.


3. Click on Customize and control Google Chrome icon once again and now select Settings.
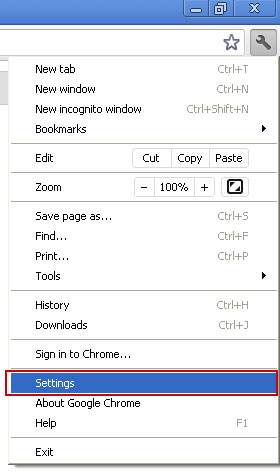


4. Click the Manage search engines... button.


5. Select Google or any other search engine you like from the list and make it your default search engine.


6. Select SweetIM Search from the list and remove it by clicking the "X" mark as shown in the image below.


And that's about it!


Associated SweetIM Toolbar files and registry values:

Files:
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\conf\logger
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\Microsoft.VC90.CRT\Microsoft.VC90.CRT.manifest
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\Microsoft.VC90.CRT\msvcm90.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\Microsoft.VC90.CRT\msvcp90.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\Microsoft.VC90.CRT\msvcr90.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\resources
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\default
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mgconfig.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mgHelperApp
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mglogger.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mgToolbarIE.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mgxml_wrapper.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\ClearHist
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mgcommon.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mgHelper.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mghooking.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mgsimcommon.dll
  • C:\Program Files\SweetIM\Toolbars\Internet Explorer\mgToolbarProxy.dll
Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\SearchScopes
  • HKEY_CURRENT_USER\Software\SweetIM\Install
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run "%ProgramFiles%\SweetIM\Communicator\SweetPacksUpdateManager.exe
  • HKEY_LOCAL_MACHINE\SOFTWARE\SweetIM\Communicator
  • HKEY_LOCAL_MACHINE\SOFTWARE\SweetIM
Tell your friends:

Friday, August 17, 2012

Remove Celas Ransomware (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Today's post is something we've been observing for several months now. Recently, we wrote about FBI and Police Central e-crime unit ransom Trojans. This time, we will take a closer look at Celas ransomware, how it has evolved over time, and how to properly remove this kind of infection.

Celas is a new company that represents the world's leading musicians. This company is owned by EMI, GEMA and PRS. If you want to learn more about it, please visit Celas official website. In short, this company stands behind popular artists or right holders and controls over how their music is used. This company is already aware of Celas virus and even made an official statement on this computer locking scam.

Unfortunately, this ransowmare is on the move at the moment. The fake Celas warning hasn't change much since we came across it for the first time, probably in April or May. But it's definitely evolving. Cyber crooks released a new variant which targets U.S. internet users. They also changed payment methods probably because they got banned from payment systems they were using previously.


There are at least five different Celas ransomware warnings that change depending on what part of the continent you are in. The structure and design elements are exactly the same for most countries but of course the wording changes. Anyway, all they trying to do with this is scare you guys to pay for something that you don't need to pay for. If you look at the ransomware you will see that are using pretty strong language. Celas ransomware claims that you were illegally downloading and distributing copyrighted songs.

Some of you guys probably might have fall for it, we know our friends have. But it's all fake. It's just a scam. If they actually caught you doing that they probably won't send you a message asking to pay $100 or euro100 to unlock your PC. That just doesn't make sense at all.

Now, if you're facing an American version of Celas ransomware, you probably noticed that there's only one way to pay the 'fine' – using Ultimate Game Card. That doesn't make sense either. You can use Ultimate Game Card to buy online games and there’s nothing wrong with this service but no one uses this service to actually pay fines. We don't know what were the main reasons why cyber criminals decided to use this service, but it doesn't look right.

The goods news is that Celas ransomware doesn't encrypt files. Other Trojans do encrypt certain files on infected computers and for this reason it usually takes longer to remove malicious files and decrypt files.

The British version is pretty much the same, except for different payment methods: Ukash and PaySafecard.

So, if you got infected with Celas ransomware, please follow the steps in the removal guide below. Normally, this malware can be removed in Safe Mode rather easily. Unfortunately, sometimes it comes bundled with other malware that locks down the computer completely. In such case, Live CD is the only option. We will show you how to remove Celas ransomware using Kaspersky Rescue Disk. Hopefully, this virus will only cost you time without taking your money too.

If you have any questions about this infection or need help removing it, please leave a comment below. Good luck!

Source: http://spywareremovalx.blogspot.com


Celas malware removal instructions:

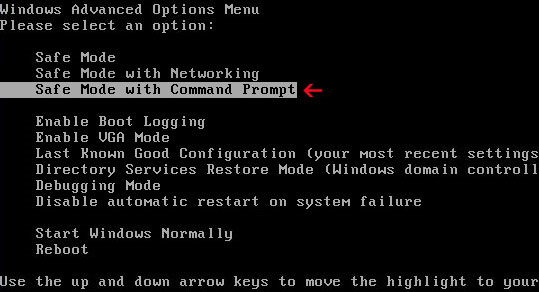
1. Reboot your computer is "Safe Mode with Command Prompt". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Command Prompt" and press Enter key. Login as the same user you were previously logged in with in the normal Windows mode.


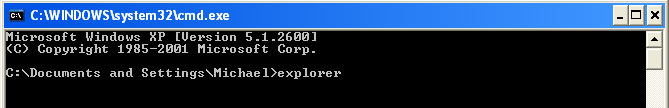
2. When Windows loads, the Windows command prompt will show up as show in the image below. At the command prompt, type explorer, and press Enter. Windows Explorer opens. Do not close it.


3. Then open the Registry editor using the same Windows command prompt. Type regedit and press Enter. The Registry Editor opens.


4. Locate the following registry entry:

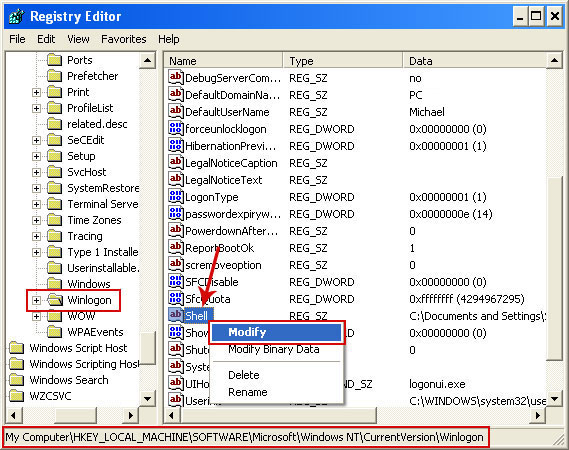
HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon\

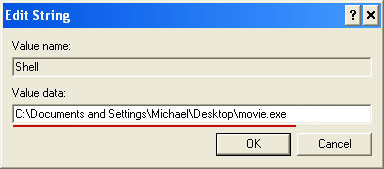
In the righthand pane select the registry key named Shell. Right click on this registry key and choose Modify.


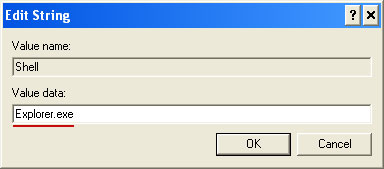
Default value is Explorer.exe.


Modified value data points to Trojan Ransomware executable file.


Please copy the location of the executable file it points to into Notepad or otherwise note it and then change value data to Explorer.exe. Click OK to save your changes and exit the Registry editor.

5. Remove the malicous file. Use the file location you saved into Notepad or otherwise noted in step in previous step.

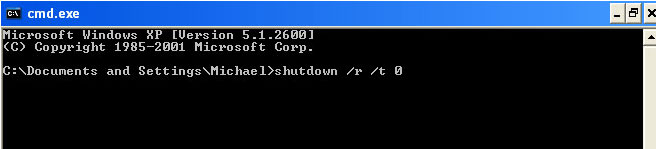
Go back into "Normal Mode". To restart your computer, at the command prompt, type shutdown /r /t 0 and press Enter.


6. Download recommended anti-malware software (Spyware Doctor) and run a full system scan to remove the leftovers of Celas ransomware from your computer.


Celas malware removal using Kaspersky Rescue Disk:

1. Download the Kaspersky Rescue Disk iso image from the Kaspersky Lab server. (Direct download link)
Please note that this is a large downloaded, so please be patient while it downloads.

2. Record the Kaspersky Rescue Disk iso image to a CD/DVD. You can use any CD/DVD record software you like. If you don't have any, please download and install ImgBurn. Small download, great software. You won't regret it, we promise.

For demonstration purposes we will use ImgBurn.

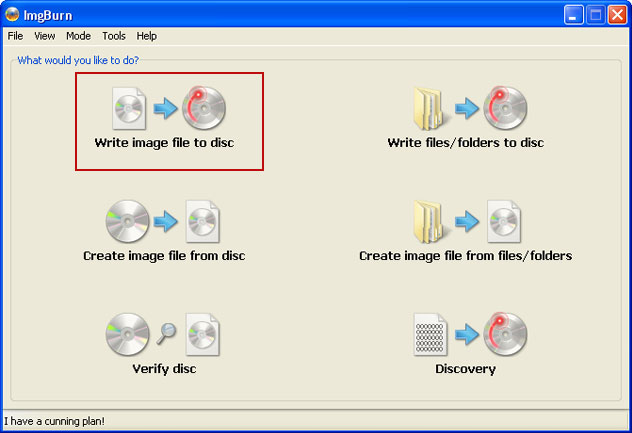
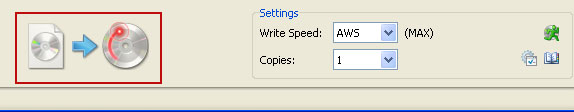
So, open up ImgBurn and choose Write image file to disc.


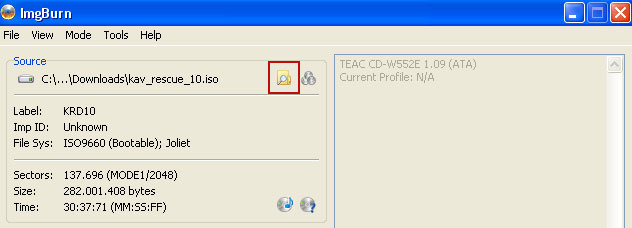
Click on the small Browse for file icon as show in the image. Browse into your download folder and select kav_rescue_10.iso as your source file.


OK, so know we are ready to burn the .iso file. Simply click the Write image file to disc button below and after a few minutes you will have a bootable Kaspersky Rescue Disk 10.


3. Configure your computer to boot from CD/DVD. Use the Delete or F2, F11 keys, to load the BIOS menu. Normally, the information how to enter the BIOS menu is displayed on the screen at the start of the OS boot.


The keys F1, F8, F10, F12 might be used for some motherboards, as well as the following key combinations:
  • Ctrl+Esc
  • Ctrl+Ins
  • Ctrl+Alt
  • Ctrl+Alt+Esc
  • Ctrl+Alt+Enter
  • Ctrl+Alt+Del
  • Ctrl+Alt+Ins
  • Ctrl+Alt+S
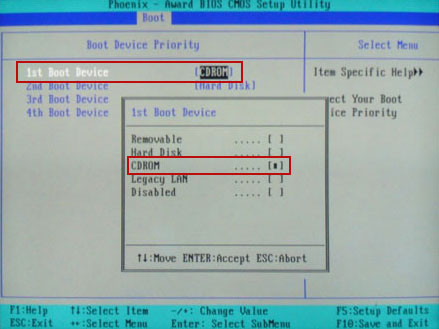
If you can enter Boot Menu directly then simply select your CD/DVD-ROM as your 1st boot device.

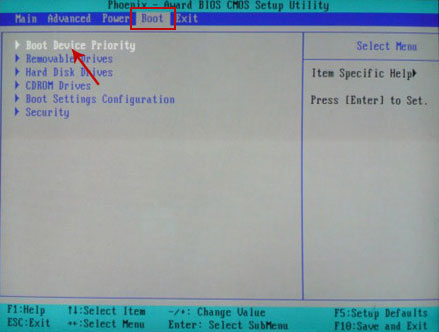
If you can't enter Boot Menu directly then simply use Delete key to enter BIOS menu. Select Boot from the main BIOS menu and then select Boot Device Priority.


Set CD/DVD-ROM as your 1st Boot Device. Save changes and exist BIOS menu.


4. Let's boot your computer from Kaspersky Rescue Disk.

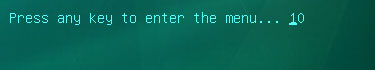
Restart your computer. After restart, a message will appear on the screen: Press any key to enter the menu. So, press Enter or any other key to load the Kaspersky Rescue Disk.


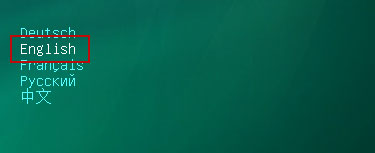
5. Select your language and press Enter to continue.


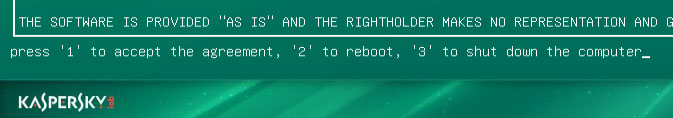
6. Press 1 to accept the End User License Agreement.


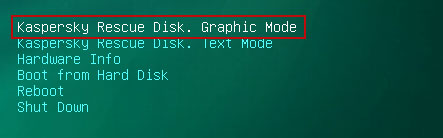
7. Select Kaspersky Rescue Disk. Graphic Mode as your startup method. Press Enter. Once the actions described above have been performed, the operating system starts.


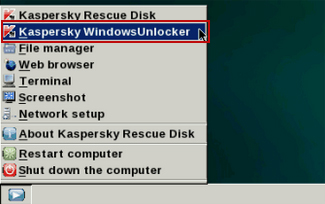
8. Click on the Start button located in the left bottom corner of the screen. Run Kaspersky WindowsUnlocker to remove Windows system and registry changes made by Celas ransomware. It won't take very long.


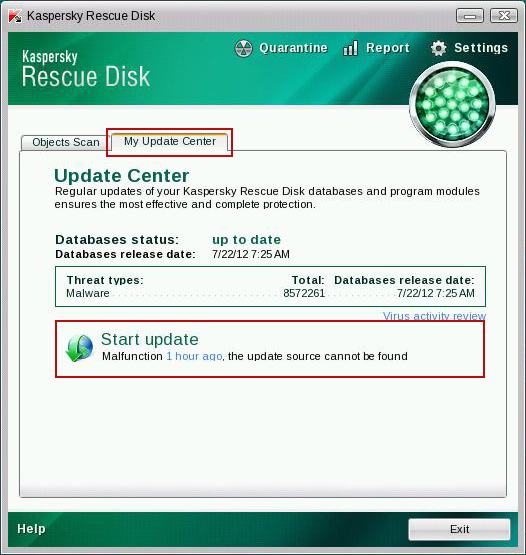
9. Click on the Start button once again and fire up the Kaspersky Rescue Disk utility. First, select My Update Center tab and press Start update to get the latest malware definitions. Don't worry if you can't download the updates. Just proceed to the next step.


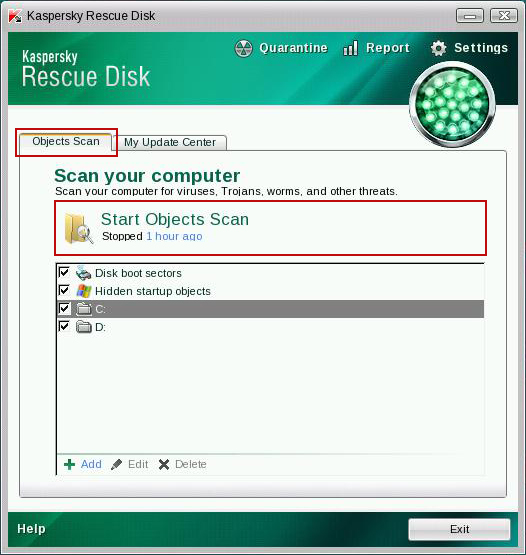
10. Select Object Scan tab. Place a check mark next to your local drive C:\. If you have two or more local drives make sure to check those as well. Then click Start Objects Scan to scan your computer for malicious software.


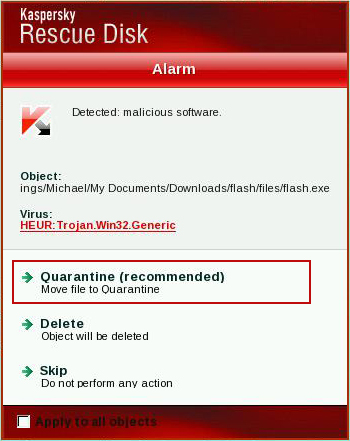
11. Quarantine (recommended) or delete every piece of malicious code detected during the system scan.


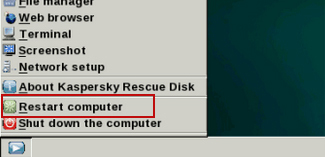
12. You can now close the Kaspersky Rescue Disk utility. Click on the Start button and select Restart computer.


13. Please restart your computer into the normal Windows mode. Download recommended anti-malware software (Spyware Doctor) and run a full system scan to remove the remnants of Celas ransomware and to protect your computer against these types of threats in the future.


Associated Celas ransomware files and registry values:

Files:
  • [SET OF RANDOM CHARACTERS].exe
Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon\"Shell" = "[SET OF RANDOM CHARACTERS].exe"
tell your friends:

Thursday, August 16, 2012

Get rid of Trojan.Dropper.Bcminer (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
A combination of ZeroAccess rootkit and Trojan.Dropper.Bcminer goes viral, at least in our state. Our friend, who has a small computer repair shop, told us he had to work overtime in order to repair all the computers that got infected with apparently the same nasty virus. This makes us wonder whether cyber crooks can target very small areas or was it just a coincidence? Too bad he didn't provide any logs from those infected machines.

We believe it could have been a legitimate self-hosted WordPress site or multiple sites hosting malware. That would make sense since all victims live in the same area and share the same interests, mostly. Besides, recently some antivirus companies reported that they have spotted a major malware campaign spread via infected WordPress websites using hidden iframes to victimize computer users. This approach is not new but still rather effective due to hundreds of thousands websites, especially self-hosted blogs, that are not being updated by their owners regularly. Malware authors can easily hide iframes and load malicious code from websites controlled by criminals; we usually call it a drive-by attack.

You can learn more about ZeroAccess rootkit here. Trojan.Dropper.Bcminer was something new to us and since our friend sent a sample of this infection to us, we decided to run it in our test environment. So, we ran the malicious file, rebooted the computer and yippee, we had a perfectly working combination of a nasty rootkit and Trojan.Dropper.Bcminer. Later we found out that a search results redirect module was also installed on our computer. What is more, Trojan.Dropper.Bcminer downloaded additional files from remote web servers which were necessary to start BitCoin mining. To learn more about BitCoins and how criminals use this legitimate service to earn money, please read this article about RiskTool.Win32.BitCoinMiner. The malicious files very requested from web sever closely related to BlackHole exploit kit. It wasn't surprising because this exploit kit is probably the most popular among cyber crooks right now.

We have to admit, that such malware combination makes sense. Cyber crooks earn money by redirecting victims to spam websites while they use their computers. When victims are away from their computers, cyber crooks use bitcoin mining modules to earn money as well. So, theoretically, they can earn money all day long.

Usually, our friend uses free malware removal tools to clean infected computers. His favorite is Malwarebytes' Antimalware. But this time, he was rather disappointed with this software because it just couldn't properly remove the infection.

As you can see in the image below, Malwarebytes finds malicious files and tries to remove them (reboot is required).


However, when the infected computer came back on, the remnants of this infection downloaded core malware components from web severs controlled by criminals and attempted to install Trojan.Bitminer and other malicious files once again. So, the Trojan.Dropper.Bcminer keeps coming back.


Running a quick system scan with other anti-malware tools clearly showed that Malwarebytes' couldn't remove malicious files from the infected computer.


C:\WINDOWS\assembly\GAC\Desktop.ini

Of course, Malwarebytes is a great tool, we use it very often but we do not rely on this single too only, you guys shouldn't either. In this case, Spyware Doctor did a great job and removed all the malicious files. To remove Trojan.Dropper.Bcminer and associated malware from your computer, please follow the removal instructions below. If you have any questions or valuable remarks, please leave a comment below. Good luck and be safe online!

http://spywareremovalx.blogspot.com


Trojan.Dropper.Bcminer removal instructions:

1. First of all, download TDSSKiller and run a system scan. This great utility will find and remove rootkits. Reboot your computer if required.

2. Then, download recommended anti-malware software (direct download) and run a full system scan to remove this virus from your computer.

Tell your friends:

Monday, August 13, 2012

Phone Shaped Pop-ups In Lower Right Hand Corner and Random Redirects (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Some of our readers have been having an awful time trying to remove malicious software that constantly redirects them to spam or even malicious websites while browsing the net and displays either a square or phone shaped pop-up in the bottom right hand corner of their web browsers. Sometimes a pop-up window resembles a video screen of ads, please see the images below.

Previously, we wrote about Trojans horses that had a very similar payload. These Trojans displayed "Recommended for You" pop-ups in the lower corner of the web browser. It actually doesn't matter which browser you use because this happens on all major web browsers, whether it would be Internet Explorer, Mozilla Firefox or Google Chrome. Cyber criminals decided to remove "Recommended for You" notification from their ads probably because victims could easily Google this text and find out that their computers are infected with malicious software. Now, they usually display a smart phone shaped ads with links and also video screen ads.

Here’s what a typical phone shaped ad looks like:


And here’s another one titled "you are missing a plugin to play videos".


A slightly different approach but we believe it's still very effective. At the time of writing, this fake fake video update ad was redirecting users to two different websites but they both promoted the same free video player. Most likely, cyber crooks earned commissions from every successful install they made. While that's clearly not the most profitable traffic monetization model we’ve seen so far, it’s still an option and cyber crooks successfully use it.

We found at least three different Trojans horses that have exactly the same payloads: web browser redirect + annoying phone shaped pop-ups. Of course, there might be hundreds of them but we were looking at the most popular ones. All these Trojans displayed pop-ups in the bottom right hand corner of the web browsers and redirected users to spam websites. Now, one of those Trojans used very aggressive methods o hide its presence on the infected computer. It even made our antivirus software to disappear. That means we have encountered different families of Trojans.

What is more, very often these Trojans come bundled with rootkits which makes the removal procedure a lot more complicated than just simply removing a Trojan horse. Most antivirus programs handle Trojan horses very well but fail to remove rootkits. Thankfully, you can use free utilities to remove rootkits from infected computers, for example TDSSKiller, if your antivirus program can't remove them.

One more thing about this infection – it changes Windows Hosts file. Normally, it doesn't lock the Hosts file itself but we've seen a couple of Trojans that not only changes the file so that it would load spammy sites but also prevent further modifications. So, if you can remove malicious lines manually, please use this great Microsoft utility called "Fix it".

To remove phone shaped pop-ups in the bottom right hand corner of your web browser, please follow the removal instructions below. Should you need any further assistance, don't hesitate to contact us or just leave a comment below. Good luck and be safe online!

http://spywareremovalx.blogspot.com


Removal instructions:

1. Download recommended anti-malware software (direct download) and run a full system scan to remove this malware from your computer.

3. To reset the Hosts file back to the default automatically, download and run Fix it and follow the steps in the Fix it wizard.

4. Remove files from Windows %Temp% folder.

Tell your friends:

Saturday, August 4, 2012

Windows Ultimate Safeguard (Removal Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
A big thank you goes to Matt from Rocky Mountains Colorado who brought our attention to a new rogue antivirus program called Windows Ultimate Safeguard. It's not a new rogue antivirus program per se, just a different name. This fake program belongs to the FakeVimes scareware family. Cyber crooks repack and rename their bogus software daily so it's rather difficult to track them all.

Matt told us he got infected with this malware yesterday. Sorry for those who fell victims to this scam. You guys probably won't get your money back unless your credit card company has some very strict regulations, etc.

Windows Ultimate Safeguard is promoted via fake online virus scanners, you know, those claiming that your computer is infected with viruses, spyware and other nasty crap. However, Matt got it from a fake video streaming website. Apperently, it was one of those fake sites that ask you to download adobeflashplayer.exe or something similar in order to watch requested video.


Once installed, this rogue antivirus program begins to scan your computer for malicious software. It may detect like ten or more infected files on your machine. But don't worry, they are all fake. Fake scans results are meant to scare you into purchasing the rogue antivirus program. DO NOT pay for it!

Windows Ultimate Safeguard disables Task manager, Resgistry editor and other system utilities. Hitting Ctr+Alt+Del brings up the rogue program instead of Task Manager.

It may associanoly block your web browser whether it would be Internet Explorer or Google Chrome. For some strange reasons it doesn't block them all the time so you may have enough time to download legitimate malware removal software.


Just like any other scareware, Windows Ultimate Safeguard displays fake security alerts. Not were aggresively thought.


The rogue program doesn't start in Safe Mode with Networking. Good news in case you can't download or run any anti-malware software in Normal Mode. Three removal methods can be used to remove Windows Ultimate Safeguard virus from your computer:
  1. Using fake registration key
  2. Using Safe Mode With Networking
  3. Removing malicious files manually
One way or another, you need to scan your computer with anti-malware software to properly remove the rogue program itself and possible remnants or additionally installed malware. Please note, it may come bundled with rootkits and other significantly sophisticated malware.

Fake payment page. Even though, it says onlineregister.com, this fake payment page is loaded from completely different location. And it's certainly not verified by Visa. 30 days money back guarantee? They just kidding.


It's surprising that after all this time, scammers haven't change they way their rogue program is registered. I mean they left the same pattern which makes it easy to generate a fake registration key. This means they probably cannot modify course code.

Anyway, if your computer got infected with this rogue antivirus program, please follow the removal instructions below. Good luck!


Windows Ultimate Safeguard removal using fake registration key:

To remove this malware using fake registration key, please follow this removal guide.


Windows Ultimate Safeguard removal using Safe Mode With Networking:

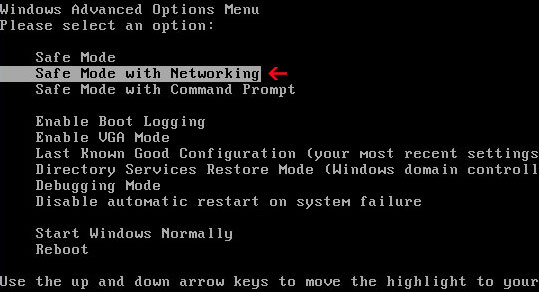
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key.


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download recommended anti-malware software (Spyware Doctor) and run a full system scan to remove Windows Ultimate Safeguard and associated malware from your computer.

NOTE: don't forget to update anti-malware software before scanning your computer.


Removing Windows Ultimate Safeguard manually:

The main malicious files is located in your Application Data folder.

Windows XP: C:\Documents and Settings\[Current User]\Application Data
Windows Vista/7: C:\Users\[Current User]\AppData\Roaming

File name: Protector-ostr.exe


Simply rename Protector-ostr.exe to virus.ex of anything you like and reboot your computer. Windows Ultimate Safeguard won't show up anymore.

Download recommended anti-malware software (Spyware Doctor) and run a full system scan to remove Windows Ultimate Safeguard and associated malware from your computer.

Tell your friends:

 
//PART 2