Monday, October 10, 2011

How to Remove Cloud Protection (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Cloud Protection is yet another rogue anti-virus product shaped like an iPhone or maybe more like an iPad just right after Jobs's death. I've just received an email from one of our readers saying just how terrible people cyber criminals can be, it's just sick, wrong. Just a few days ago they released Guard Online malware and now there's an exact copy of this malware attempting to lure people into paying for completely useless security product. As we said before, Cloud Protection can not protect your computer from hackers, viruses, scams, and other security threats. Just because it looks nice doesn't mean anything. It can't remove viruses, spyware and other malicious software, so don't even think about purchasing it. Fake AVs continue to be more prevalent than any other type of virus trying to lure people into obtain credit card details. If your computer is infected with Cloud Protection, please follow the steps in the removal guide below.


OK, so, just like the previous version of this scareware, Cloud Protection will actually drop a rootkit onto your computer. It's the ZeroAccess rootkit. This rootkit is being distributed very actively, thankfully, there at least a couple of tools that can handle this very sophisticated malware. You can use either TDSSKiller or ZeroAceess removal tool by Webroot. Both are completely free, except the the second one does't work on 64-bit systems. Anyway, to remove Cloud Protection from your computer, please follow the removal instructions below. And one more thing, if you choose to remove this virus manually, you should still run a full system scan with anti-malware tool and TDSSKiller. If you have any questions, please leave a comment below. Good luck and be safe online!

http://spywareremovalx.blogspot.com


Cloud Protection removal instructions:

1. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

If you can't download it, please reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Open Internet Explorer and download STOPzilla. Once finished, go back into Normal Mode and run it. That's It!

Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
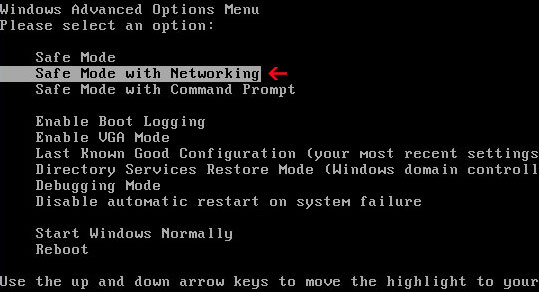

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Remove the TDSS/ZeroAccess rootkit (if exists). Please follow this removal guide: http://spywareremovalx.blogspot.com/2010/03/tdss-alureon-tidserv-tdl3-removal.html


Manual Cloud Protection removal guide:

1. Right-click on Guard Online icon and select Properties. Then select Shortcut tab.

The location of the malware is in the Target box.

2. In our case the malicious file was located in C:\Windows\System32 folder. Select the malicious file, rename it and change a file name extension.

Original file: TcS22bF3nGaQWKf.exe


Renamed file: TcS22bF3nGaQWKf.vir
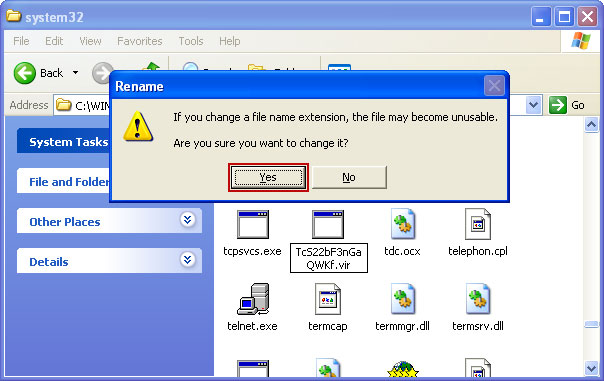


3. Restart your computer. After a reboot, download free anti-malware software from the list below and run a full system scan.

4. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

5. Remove the TDSS/ZeroAccess rootkit (if exists). Please follow this removal guide: http://spywareremovalx.blogspot.com/2010/03/tdss-alureon-tidserv-tdl3-removal.html


Manual activation and Cloud Protection removal:

1. Choose to remove threats and manually activate the rogue program. Enter one of the following codes to activate Cloud Protection.

9992665263
1148762586
1171249582
1186796371
1196121858
1225242171
1354156739
1579859198
1789847197
1835437232
1837663686
1961232582

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. Remove the TDSS/ZeroAccess rootkit (if exists). Please follow this removal guide: http://spywareremovalx.blogspot.com/2010/03/tdss-alureon-tidserv-tdl3-removal.html


Associated Cloud Protection files and registry values:

Files:
  • C:\WINDOWS\system32\[SET OF RANDOM CHARACTERS].exe
  • C:\Documents and Settings\[UserName]\Application Data\csrss.exe
  • C:\Documents and Settings\[UserName]\Application Data\hTrkd58DeORldrQCloud Protection.ico
  • C:\Documents and Settings\[UserName]\Application Data\Microsoft\csrss.exe
  • C:\Documents and Settings\[UserName]\Desktop\Cloud Protection.lnk
  • C:\Documents and Settings\[UserName]\Local Settings\Temp\[SET OF RANDOM CHARACTERS].tmp
  • C:\Documents and Settings\[UserName]\Start Menu\Programs\Cloud Protection\Cloud Protection.lnk
Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
Share this information with your friends:

Saturday, October 8, 2011

How to Remove Guard Online (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Guard Online is a re-branded and re-designed version of the AV Guard Online scareware. It does the usual stuff -- displays fake virus alerts claiming that your computer is infected with spyware, Trojans, and other malcode and blocks legitimate security products and Windows utilities. Buying rogue antivirus program won't help because it can't remove anything and it obviously won't protect your computer against emerging security threats, you know, viruses, spam emails, keyloggers, etc. However, malware creators are constantly coming up with new ways to deceive people into paying for bogus security products. Just take a look at this rogue. It's an iPad. Guard Online looks almost exactly the same. I find it truly disrespectful that they decided to make such rogue in the context of the recent news about Steve Jobs.


But that's not all, cyber criminals decided that it would be a lot better to drop a rootkit from the notorious TDSS malware family to make the removal procedure a lot more complicated. To remove Guard Online from your computer, please follow the removal instructions below. Although, the removal guide was originally created to help you to remove the AV Guard Online scareware, this guide identifies the procedures to be followed to ensure appropriate Guard Online removal as well. If you have any questions, please leave a comment below. Good luck and be safe online!

http://spywareremovalx.blogspot.com


Guard Online removal instructions:

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. Remove the TDSS rootkit (if exists). Please follow this removal guide: http://spywareremovalx.blogspot.com/2010/03/tdss-alureon-tidserv-tdl3-removal.html


Manual Guard Online removal guide:

1. Right-click on Guard Online icon and select Properties. Then select Shortcut tab.

The location of the malware is in the Target box.

2. In our case the malicious file was located in C:\Windows\System32 folder. Select the malicious file, rename it and change a file name extension.

Original file: TcS22bF3nGaQWKf.exe


Renamed file: TcS22bF3nGaQWKf.vir


3. Restart your computer. After a reboot, download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

4. Remove the TDSS rootkit (if exists). Please follow this removal guide: http://spywareremovalx.blogspot.com/2010/03/tdss-alureon-tidserv-tdl3-removal.html


Manual activation and Guard Online removal:

1. Choose to remove threats and manually activate the rogue program. Enter one of the following codes to activate AV Guard Online.

9992665263
1148762586
1171249582
1186796371
1196121858
1225242171
1354156739
1579859198
1789847197
1835437232
1837663686
1961232582

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. Remove the TDSS rootkit (if exists). Please follow this removal guide: http://spywareremovalx.blogspot.com/2010/03/tdss-alureon-tidserv-tdl3-removal.html


Associated Guard Online files and registry values:

Files:

  • C:\WINDOWS\system32\[SET OF RANDOM CHARACTERS].exe
  • C:\Documents and Settings\[UserName]\Application Data\csrss.exe
  • C:\Documents and Settings\[UserName]\Application Data\hTrkd58DeORldrQGuard Online.ico
  • C:\Documents and Settings\[UserName]\Application Data\Microsoft\csrss.exe
  • C:\Documents and Settings\[UserName]\Desktop\Guard Online.lnk
  • C:\Documents and Settings\[UserName]\Local Settings\Temp\[SET OF RANDOM CHARACTERS].tmp
  • C:\Documents and Settings\[UserName]\Start Menu\Programs\Guard Online\Guard Online.lnk

Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
Share this information with your friends:

Steve Jobs Alive! Spam, Win32/Waledac.C Trojan and Spambot

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Steve Jobs' death is an enormous loss for all of us. Sadly, there are some people who exploited the death of Steve Jobs. They took the advantage of those shocked and moved by such a sad bit of news. Cyber criminals behind a botnet (Waledac?) mostly involved in e-mail spam were sending sending spam emails and distributing Trojan downloaders. The spam email has one of the following subjects:
  • Steve Jobs Alive!
  • Steve Jobs: Not Dead Yet!
  • Is Steve Jobs Really Dead?
  • Steve Jobs Not Dead!
Here's what the spam email looks like:


As you can see, scammers claim that Steve Jobs is alive and highly suggest you check it out. Clicking on the link provided will take you to a malicious website which distributes TrojanDownloader:Win32/Waledac.C [Microsoft]. Once installed, the Trojan downloader will request other malicious files from the Internet and eventually will turn your computer to another spamming machine (Spambot). Currently the detection rate is very low. Please think carefully about the links that you click on. Good luck and be safe online!

Share this information with your friends:

Thursday, October 6, 2011

Use Priv3 to Prevent Being Tracked by Social Networks

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
I use Facebook almost daily and I'm sure that for most of us it would be rather frustrating to have that taken away. Privacy is a major concern for lots of members. And we all know how Facebook grapples with privacy issues. I believe there will be even more privacy issues in the feature. However, I didn't know that Facebook can track your visits to other websites that have implemented "Like" or "Follow" buttons. Of course, it's possible only when you are logged into your Facebook account but you don't even have to click on either of these buttons. How rude!

All my favorites websites are integrated with Facebook, including this blog. The same can be said for websites like Twitter, Google Plus or LinkedIn. They can track your visits to other websites too. By the way, Google's +1 is becoming increasingly popular button as well.

So, if you're concerned about privacy, I highly recommend this installation. What it does is protect you from being tracked by social networks. It's a small but very useful Mozilla Firefox extension called Priv3. The best part is that Priv3 doesn't completely block social networking features. There won't be any negative impact on your interaction with social networks. It's funded by the National Science Foundation and developed by folks at Berkeley university. If you want to learn more about the Priv3 project, please visit the official website.


A screenshot of Priv3

You should also read our previous article Facebook Security and Privacy Best Practices to learn more about Facebook privacy settings and how to avoid Facebook scams. We also created a short guide on how to install Priv3 extension in Mozilla Firefox web browser. Please follow the steps in our installation guide below. Surf the Web with improved privacy. Good luck!

NOTE: before installing Priv3, please update your web browser but this extension is not compatible with older versions of Mozilla Firefox.


How to install Priv3

1. Go to http://priv3.icsi.berkeley.edu. Click on Install button.


2. Mozilla Firefox will display a notification as show in the image below. Please click Allow button to continue.


3. Click on Install Now button to install Priv3 extension.


4. Priv3 will be installed after you restart Firefox. Click on Restart Now button or just close your web browser. To view Priv3 icon, please enable Addon bar.


How to uninstall Priv3

1. Open Mozilla Firefox. Go to Tools → Add-ons.


2. Select Extensions. Choose Priv3 and click on Remove button.


Share this information with your friends:

How to Remove AV Guard Online (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
AV Guard Online is a fake anti-virus program that displays annoying pop-up messages claiming that viruses, Trojans, and other malicious software have been found, and offering to sell you a worthless solution. You should really beware of fake anti-virus software. Celebrity gossip, rumors, stolen tapes, infected adult websites and similar stuff usually lead users to malicious websites. We were actually very happy because of a significant drop in fake antivirus distribution activity. The authorities had taken down two distinct scam networks, there were only a few rogue anti-virus incidents during the last few weeks in your organization. Unfortunately, it's far too early to celebrate because cyber crooks came back with some fresh ideas and new viruses. On the other hand, rootkits and other more sophisticated malware took the lead and I'm not really sure what is worse. I've see a lot of posts out there about AV Guard Online already but only a few of them were created solely to help you to remove AV Guard Online malware without actually asking you to pay for commercial anti-malware software. I'm going to pass on a few words of wisdom, and while this may read like another "how to remove/get rid of", I'll show you some tricks that can make removal procedure a lot easier. To remove AV Guard Online from your computer, please follow the removal instructions below.


Before we continue, let's have a look at some of the fake security alerts and pop-ups designed to scare you into thinking that your computer is infected by Trojans and similar stuff. The graphical users interface is rather professional, but you can still tell it's a fake anti-virus program because genuine security products usually do not flash like very one or two minutes and do not block Windows system utilities. AV Guard Online reports the same infections on every infected computer, six threats including Trojan.VBS.Qhost, Trojan-Downloaded.JS.Remora and some others.

Here's an interesting fake security alerts claiming that your computer is infected by Keylogger Zeus malware.
Warning! Infection found
Unwanted software (malware) or tracking cookies have been found during last scan. It is highly recommended to remove it from your computer.
Keylogger Zeus was detected and put in quarantine.
Keylogger Zeus is a very dangerous software used by criminals to steal personal data such as credit card information, access to banking accounts, passwords to social networks and e-mails.


Nice, isn't it. There are some regular misleading pop-ups too.
Warning!
The file "taskmgr.exe" is infected. Running of application is impossible.
Please activate your antivirus software.

Security Warning
There are critical system files on your computer that were modified by malicious software.
It may cause permanent data loss.
Click here to remove malicious software.


And here's the whole list of supposedly infected items.


AV Guard Online is good at hiding from anti-virus programs. You're going to need to do a few things to make the system usable again. We wrote three different removal guides: manual removal guide, manual activation and the regular one using free anti-malware software. It is also worth mentioning that AV Guard Online can not delete your files and steal your sensitive information unless it comes bundled with more sophisticated malware. Most of the time it doesn't so do not worry. Oh, and one more thing, do not reboot your computer multiple times letting the infection dig deeper and deeper. Just follow the removal instructions below and you should be able to remove AV Guard Online without any problems. As always, if you have any questions, please leave comments below or just email us. Good luck and be safe online!

http://spywareremovalx.blogspot.com

AV Guard Online removal instructions:

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.


Manual AV Guard Online removal guide:

1. Right-click on AV Guard Online icon and select Properties. Then select Shortcut tab.


The location of the malware is in the Target box.


2. In our case the malicious file was located in C:\Windows\System32 folder. Select the malicious file, rename it and change a file name extension.

Original file: TcS22bF3nGaQWKf.exe


Renamed file: TcS22bF3nGaQWKf.vir


3. Restart your computer. After a reboot, download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.


Manual activation and AV Guard Online removal:

1. Choose to remove threats and manually activate the rogue program. Enter one of the following codes to activate AV Guard Online.

9992665263
1148762586
1171249582
1186796371
1196121858
1225242171
1354156739
1579859198
1789847197
1835437232
1837663686
1961232582


2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.


Associated AV Guard Online files and registry values:

Files:

  • C:\WINDOWS\system32\[SET OF RANDOM CHARACTERS].exe
  • C:\Documents and Settings\[UserName]\Application Data\conhost.exe
  • C:\Documents and Settings\[UserName]\Application Data\csrss.exe
  • C:\Documents and Settings\[UserName]\Application Data\[SET OF RANDOM CHARACTERS].1B6
  • C:\Documents and Settings\[UserName]\Application Data\ldr.ini
  • C:\Documents and Settings\[UserName]\Application Data\zA0uvS2ib3m5Q6EAV Guard Online.ico
  • C:\Documents and Settings\[UserName]\Application Data\Microsoft\csrss.exe
  • C:\Documents and Settings\[UserName]\Desktop\AV Guard Online.lnk
  • C:\Documents and Settings\[UserName]\Local Settings\Temp\[SET OF RANDOM CHARACTERS].tmp
  • C:\Documents and Settings\[UserName]\Local Settings\Temp\[SET OF RANDOM CHARACTERS].tmp
  • C:\Documents and Settings\[UserName]\Start Menu\Programs\AV Guard Online\AV Guard Online.lnk

Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run "[SET OF RANDOM CHARACTERS]"
Share this information with your friends:

 
//PART 2