Tuesday, February 1, 2011

Windows Problems Remover, Windows Health Center, Windows Shield Center Removal Instructions

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Just a few days ago we reported finding the Windows Antispyware Solution scareware and today we came across another three different names for basically the same Trojan that pretends to be legitimate security software: Windows Problems Remover, Windows Health Center and Windows Shield Center (and there are even more names, see list below). It's not especially noteworthy because we have posted multiple articles about this rogue program in a last few months. The rogue program impersonates legitimate security software, reports false scan results and asks to pay for a full version of the program to remove the threats. It blocks other programs on your computer and displays fake security warnings. If you somehow ended up with Windows Problems Remover, Windows Health Center or Windows Shield Center malware, please follow the steps in the removal guide below to remove it from your computer. Please read our previous post about Windows Security & Control for more detailed analysis. The methodology and removal instructions are basically the same for this rogue program not matter how it calls itself. If you have any questions, please leave a comment. Good luck and be safe online!

Cyber-criminals change rogues' names very often. This removal guide run under quite a few different names, which I have listed below:

Rogue Names:
Windows Passport Utility Windows Stability Center Windows Process Regulator
Windows Power Expansion Windows Simple Protector Windows Expansion System
Windows Background Protector Windows Support System Windows Emergency System
Windows Efficiency Magnifier Windows Threats Removing Windows Remedy
Windows Troubles Remover Windows Servant System Windows Defence Center
Windows Error Correction Windows Debug System Windows Perfomance Manager
Windows Troubles Analyzer Windows Processes Organizer Windows Privacy Agent
Windows Express SettingsWindows Optimal Tool Windows Safety Guarantee
Windows AV Software Windows Express Help Windows User Satellite
Windows Optimal Settings Windows Optimal Solution Windows Care Tool
Windows Wise Protection Windows Software Guard Windows Software Protection
Windows Safety Protection Windows Problems Protector Windows Lowlevel Solution

Windows Troubles Remover


Windows Privacy Agent


Windows Care Tool


Removal instructions:

1. Rename the main executable of the rogue program:

In Windows XP:
C:\Documents and Settings\[UserName]\Application Data\[SET OF RANDOM CHARACTERS].exe
C:\Documents and Settings\[UserName]\Application Data\Microsoft\[SET OF RANDOM CHARACTERS].exe

In Windows Vista/7:
C:\Users\[UserName]\AppData\Roaming\[SET OF RANDOM CHARACTERS].exe
C:\Users\[UserName]\AppData\Roaming\Microsoft\[SET OF RANDOM CHARACTERS].exe


Alternate location:


Look for xmrmuy or similar file and rename it to malware. Then restart your computer. This should disable the rogue program. After reboot, please continue with the rest of the removal process. NOTE: By default, Application Data folder is hidden. If you can find it, please read Show Hidden Files and Folders in Windows.

OR you can download Process Explorer and end rogue's process.


2. Download shell-fix.reg. Double-click to run it. Click "Yes" when it asks if you want to add the information to the registry. This file will fix the Windows Shell entry.
3. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus.


Alternate removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
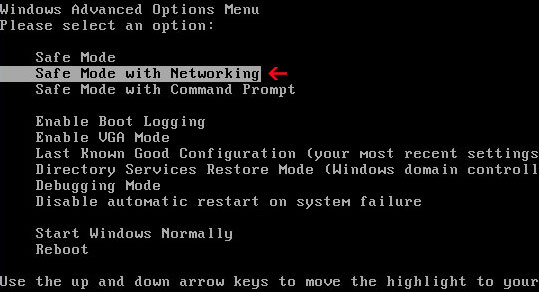

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus.


Associated files and registry values:

Files:

In Windows XP:
  • C:\Documents and Settings\[UserName]\Application Data\[SET OF RANDOM CHARACTERS].exe
  • C:\Documents and Settings\[UserName]\Application Data\Microsoft\[SET OF RANDOM CHARACTERS].exe
In Windows Vista/7:
  • C:\Users\[UserName]\AppData\Roaming\[SET OF RANDOM CHARACTERS].exe
  • C:\Users\[UserName]\AppData\Roaming\Microsoft\[SET OF RANDOM CHARACTERS].exe
Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows NT\CurrentVersion\Winlogon "Shell" = '%UserProfile%\Application Data\[SET OF RANDOM CHARACTERS].exe'
  • HKEY_CURRENT_USER\Software\Microsoft\Windows NT\CurrentVersion\Winlogon "Shell" = '%UserProfile%\Application Data\Microsoft\[SET OF RANDOM CHARACTERS].exe'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\egui.exe "Debugger" = 'svchost.exe'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\ekrn.exe "Debugger" = 'svchost.exe'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\msascui.exe "Debugger" = 'svchost.exe'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\msmpeng.exe "Debugger" = 'svchost.exe'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\msseces.exe "Debugger" = 'svchost.exe'
Share this information with other people:

Monday, January 31, 2011

How to Remove Fake AVG Antivirus 2011 (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Today we came across another rogue program called AVG Antivirus 2011. Please do not confuse this malware with the legitimate anti-virus program called AVG Anti-virus. It's not the first time when cyber-criminals use names and other copyrighted materials of well-known and trusted antivirus manufacturers to mislead inexperienced Internet users. The fake AVG Antivirus 2011 is a clone of Antivirus 8. We got it from a fake online scanner but this scareware might be distributed via trojan downloaders and other malware too. Just like all the other rogue security programs, the fake AVG Antivirus 2011 reports false system security threats to make you think that your computer is infected with malicious software: viruses, trojans, worms, adware and other viruses. It found 25 infections on our test machine but of course it was absolutely clean (expect the rogue program obviously). As a typical scareware, it will prompt you to register the program in order to remove the threats. The price may vary from $50 to $100. You can get a fully functional internet security suite for such price. Don't even consider buying this piece of malware. We've got the removal instructions to help you to remove AVG Antivirus 2011 from your computer for free. Please follow the removal instructions below.


Thanks to rogueamp for making this video.

When running, AVG Antivirus 2011 will display numerous fake security alerts saying "Warning! Active virus detected!" or "Warning! Identity theft attempt detected!". It usually displays such warnings on attempt to run perfectly legitimate programs. For example, it may detect notepad.exe as keylogger or some other malware. This fake AV state that your Windows product key can be stolen.


AVG Antivirus 2011 hijacks web browsers as well and generates fake security warnings. There are mainly two: Internet Explorer Emergency Mode and Attention! Your web page requested has been canceled.
About Internet Explorer Emergency Mode
Your PC is infected with malicious software and browse couldn't be launched
You may use Internet Explorer in Emergency mode - internal service browser of Microsoft Windows system with limited usability.
Notice: Some sites refuse connection with Internet Explorer in Emergency Mode. In such case system warning page will be showed to you.


To sum things up, AVG Antivirus 2011 is a rogue security program that has nothing to do with the legitimate anti-virus program called AVG Anti-virus. It blocks other programs on your computer, hijacks web browsers and displays annoying security alerts about non-existent security threats. It reports false infections and prompts to pay for a full version of the rogue program to remove them. It doesn't have any official website and doesn't provide any contact information. Last, but not least, this fake AVG Antivirus 2011 is promoted through the use of other malware. I think it's obvious that AVG Antivirus 2011 is a scam. If you have already purchased this rogue anti-virus, please contact your credit card company and dispute the charges. To remove AVG Antivirus 2011, please follow the step in the removal guide below. If you have something to add about this threat, please leave a comment. Tell your friends about this infection. Good luck and be safe online!

UPDATE: You can use one of the codes listed below to register the fake AVG Antivirus 2011 (no personal information required). Then scan your computer with anti-malware software.

KNI75-MLM57-CBP65-GPB229-XYL05
NNI90-KOJ66-BCD37-CPA123-XYL21
NDM92-LJD85-IFI74-ODK303-XYL25
AOC55-KBF04-COF00-FAO235-XYL05
DLK35-JNC21-KDF83-CBL035-XYL73
LOD37-GPF25-KKO37-MKM115-XYL44


AVG Antivirus 2011 activation notice:


AVG Antivirus 2011 removal instructions:

Download recommended anti-malware software (direct download) and run a full system scan to remove this virus from your computer.

NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

If you can't download it, please reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. That's It!

Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.


AVG Antivirus 2011 removal instructions (Manual):

1. Go into C:\WINDOWS\system32 folder. Locate iesafemode.exe and delete it.


2. Open the Windows Registry Editor. At the taskbar, click Start → Run. Type regedit and click OK or press Enter. (In Windows Vista/7 click the Start button in the lower-left corner of your screen. Type regedit into Start search box and press Enter).


3. Locate the HKEY_LOCAL_MACHINE entry: HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\iexplore.exe

In the righthand pane select Debugger = iesafemode.exe -sb and delete it if it exists.
Close the registry editor.


4. Download recommended anti-malware software (direct download) and run a full system scan to remove this virus from your computer.

NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.


Associated AVG Antivirus 2011 files and registry values:

Files:
  • C:\Documents and Settings\All Users\Start Menu\AVG Antivirus 2011\
  • C:\Documents and Settings\All Users\Start Menu\AVG Antivirus 2011\AVG Antivirus 2011.lnk
  • C:\Documents and Settings\All Users\Start Menu\AVG Antivirus 2011\Uninstall.lnk
  • C:\Program Files\AVG Antivirus 2011\
  • C:\Program Files\AVG Antivirus 2011\avg.exe
  • C:\WINDOWS\system32\iesafemode.exe
Registry values:
  • HKEY_CURRENT_USER\Software\[SET OF RANDOM CHARACTERS]
  • HKEY_CURRENT_USER\Software\[SET OF RANDOM CHARACTERS]
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\chrome.exe
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\firefox.exe
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\iexplore.exe
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\opera.exe
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\safari.exe
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "AVG Antivirus 2011" = 'C:\Program Files\AVG Antivirus 2011\avg.exe'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\User Agent\Post Platform "WinNT-A8I 28.01.2011"
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\chrome.exe "Debugger" = 'iesafemode.exe -sb'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\firefox.exe "Debugger" = 'iesafemode.exe -sb'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\iexplore.exe "Debugger" = 'iesafemode.exe -sb'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\opera.exe "Debugger" = 'iesafemode.exe -sb'
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\safari.exe "Debugger" = 'iesafemode.exe -sb'
Share the knowledge:

Saturday, January 29, 2011

How to Remove Smart Internet Protection 2011 (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Smart Internet Protection 2011 is a rogue security program that shows false scan results and stops most programs running on your computer to make you think that you are infected with some sort of malware. The whole purpose of this scareware is to trick you into actually making a purchase of this bogus software. It doesn't steal or delete any of your data. Don't worry about that. Smart Internet Protection 2011 was first noticed on January 27th. It's a clone of Personal Internet Security 2011. We wrote about this rogue program one month ago and it looks like Smart Internet Protection 2011 is here to replace it. As a typical fake anti-virus program, it pretends to scan your computer for malcode. Smart Internet Protection 2011 creates 15-20 harmless files on your computer and then "flags" those files as infections, e.g. spyware, trojans, adware and other viruses: Trojan-PSW.VBS.Half, SpamTool.Win32.Delf.h, Trojan-IM.Win32.Faker.a and some other names. I'm sure this rogue program will display the same names for you too that's because it doesn't actually scan your computer. If don't know how to remove Smart Internet Protection 2011 from your computer then please follow the removal instructions below.


Smart Internet Protection 2011 will be configured to start automatically. It changes certain Windows registry keys and adds a new start-up process. This rogue hijacks Internet Explorer and changes Local Area Connection settings to use a proxy server that will not allow you to browse almost any web pages. Smart Internet Protection 2011 will change your default search page to findgala.com that's probably because the developers of the rogue program are affiliated with this search page. What is more, it will modify Windows Hosts file and changes its permission so that you couldn't edit it. Furthermore, Smart Internet Protection 2011 will display fake security warnings about identity thefts attempts and dangerous infections that may cause serious damage to the system. Please ignore any of the scan results and security alerts this program displays. This application was only created to trick you into purchasing it. It provides false sense of security. You should not purchase it, and if you have, please contact your credit card company and dispute the charges. To remove Smart Internet Protection 2011 and any related malware, please follow the steps in the removal instructions below. Please tell your friends about this threat. If you have any questions about this rogue program, please leave a comment. Good luck and be safe online!


Smart Internet Protection 2011 removal instructions:

1. Reboot your computer is "Safe Mode with Networkin>g". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Launch Internet Explorer. In Internet Explorer go to: Tools->Internet Options->Connections tab. Click Lan Settings button and uncheck the checkbox labeled Use a proxy server for your LAN. Click OK. You may have to repeat steps 1-2 if you will have problems downloading malware removal programs.


3. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Alternate Smart Internet Protection 2011 removal instructions using HijackThis or Process Explorer (in Normal mode):

1. Launch Internet Explorer. In Internet Explorer go to: Tools->Internet Options->Connections tab. Click Lan Settings button and uncheck the checkbox labeled Use a proxy server for your LAN. Click OK.


2. Download Process Explorer.
3. Rename procexp.exe to iexplore.exe and run it. Look for similar process in the list and end it:
  • SI20e_289.exe
OR download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro).
Launch the iexplore.exe and click "Do a system scan only" button.
If you can't open iexplore.exe file then download explorer.scr and run it. Search for similar entries in the scan results:

R1 - HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=127.0.0.1:25775
O4 - HKCU\..\Run: [Smart Internet Protection 2011] "C:\Documents and Settings\All Users\Application Data\20eab6\SI20e_289.exe" /s /d
Select all similar entries and click once on the "Fix checked" button. Close HijackThis tool.

4. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

5. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Smart Internet Protection 2011 associated files and registry values:

Files:
  • C:\Documents and Settings\All Users\Application Data\20eab6\
  • C:\Documents and Settings\All Users\Application Data\20eab6\SI20e_289.exe
  • C:\Documents and Settings\All Users\Application Data\20eab6\35.mof
  • C:\Documents and Settings\All Users\Application Data\20eab6\[SET OF RANDOM CHARACTERS].dll
  • C:\Documents and Settings\All Users\Application Data\sqhdr5\[SET OF RANDOM CHARACTERS].ocx
  • C:\Documents and Settings\All Users\Application Data\SMEYFE
  • %UserProfile%\Application Data\Smart Internet Protection 2011\
%UserProfile% refers to:
C:\Documents and Settings\ (for Windows 2000/XP)
C:\Users\[User Name]\AppData (for Windows Vista & Windows 7)

Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "RunInvalidSignatures" = '1'
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings "ProxyServer" = "http=127.0.0.1:25775"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "Smart Internet Protection 2011"
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Image File Execution Options "Debugger" = "svchost.exe"
Share this information with other people:

How to Remove Windows Antispyware Solution (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Windows Antispyware Solution is a rogue program that pretends to scan and detect malware and other problems on your computer. It is distributed mainly through software exploits and Trojans. The rogue program is also promoted via fake online scanners and infected adult websites. Once installed, Windows Antispyware Solution will prompt you to remove the false threat detections that appeared during your computer scan. Then it will take you directly to a registration form in order to buy the product. Furthermore, Windows Antispyware Solution will block nearly all programs on your computer including task manager and other system utilities. It will state that task manager was terminated because it is infected with some sort of malware that may steal your sensitive information. Windows Antispyware Solution will display fake security alerts and hide your desktop icons/task bar. This program is a scam. If you got hit with this malware, please follow the removal instructions below to remove Windows Antispyware Solution as soon as you can. Last, but not least, if you have paid for a full version of this fake application, please contact your credit card company and dispute the charges. Good luck and be safe online!

Windows Antispyware Solution is from the same family as Windows Risk Eliminator and Windows Utility Tool. It's not a virus. This scareware cannot delete your files or steal your sensitive information.


Windows Antispyware Solution removal instructions:

1. Rename the main executable of Windows Antispyware Solution:

In Windows XP:
C:\Documents and Settings\[UserName]\Application Data\[SET OF RANDOM CHARACTERS].exe

In Windows Vista/7:
C:\Users\[UserName]\AppData\Roaming\[SET OF RANDOM CHARACTERS].exe


Look for jycxxf or similar file and rename it to malware. Then restart your computer. This should disable Windows Antispyware Solution. After reboot, please continue with the rest of the removal process. NOTE: By default, Application Data folder is hidden. If you can find it, please read Show Hidden Files and Folders in Windows.

OR you can download Process Explorer and end Windows Universal Tool process.


2. Download shell-fix.reg. Double-click to run it. Click "Yes" when it asks if you want to add the information to the registry. This file will fix the Windows Shell entry.
3. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus.


Alternate Windows Antispyware Solution removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus.


Associated Windows Antispyware Solution files and registry values:

Files:

In Windows XP:
  • C:\Documents and Settings\[UserName]\Application Data\[SET OF RANDOM CHARACTERS].exe
In Windows Vista/7:
  • C:\Users\[UserName]\AppData\Roaming\[SET OF RANDOM CHARACTERS].exe
Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows NT\CurrentVersion\Winlogon "Shell" = "%UserProfile%\Application Data\[SET OF RANDOM CHARACTERS]"
Share this information with other people:

Thursday, January 27, 2011

How to Remove Windows Risk Eliminator (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Windows Risk Eliminator is a malicious program that uses a number of misleading techniques to make a hefty profit out of unsuspecting victims. This program is classified as a rogue security tool because it pretends to scan your computer for malware and reports system threats which do not even exist. Cyber-criminals spread their malware through the use of Trojan Downloader and fake online scanners. Victims are typically tricked into paying for additional tools or services. This rogue costs almost $80 with a lifetime support. You can get perfectly legitimate anti-malware software for about $40. Windows Risk Eliminator gives a false sense of security. It displays fake security alerts and notifications saying that your computer is infected with some sort of malware. Furthermore, Windows Risk Eliminator claims that you can make your computer run faster if you pay for a additional tools that will fix numerous system/registry errors. Please do not fall victim to this scam and remove Windows Risk Eliminator from your computer as soon as possible. What is more, this scareware blocks other programs on the victim's computer. It blocks web browsers, task manager, registry editor and of course anti-malware software. Thankfully, we've got the step-by-step removal instructions to help you to remove Windows Risk Eliminator malware. Last, but not least, if you have purchased this bogus program, please contact your credit card company and dispute the charges. If you need help removing Windows Risk Eliminator, please leave comment. You can post additional information about this rogue too. Good luck and be safe online!

Windows Risk Eliminator is from the same family as Windows Universal Tool, Windows Utility Tool, and Windows Security & Control.


Fake Windows Risk Eliminator scan results:


Fake security alert saying that taskmgr.exe is a key-logger:


A web form where you can purchase Windows Risk Eliminator:


Windows Risk Eliminator removal instructions:

1. Rename the main executable of Windows Risk Eliminator:

In Windows XP:
C:\Documents and Settings\[UserName]\Application Data\[SET OF RANDOM CHARACTERS].exe

In Windows Vista/7:
C:\Users\[UserName]\AppData\Roaming\[SET OF RANDOM CHARACTERS].exe


Look for htwlfy or similar file and rename it to malware. Then restart your computer. This should disable Windows Risk Eliminator. After reboot, please continue with the rest of the removal process. NOTE: By default, Application Data folder is hidden. If you can find it, please read Show Hidden Files and Folders in Windows.

OR you can download Process Explorer and end Windows Risk Eliminator process.

2. Download shell-fix.reg. Double-click to run it. Click "Yes" when it asks if you want to add the information to the registry. This file will fix the Windows Shell entry.
3. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus.


Alternate Windows Risk Eliminator removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download free anti-malware software from the list below and run a full system scan.
NOTE: in some cases the rogue program may block anti-malware software. Before saving the selected program onto your computer, you may have to rename the installer to iexplore.exe or winlogon.exe With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET NOD32 Antivirus.


Associated Windows Risk Eliminator files and registry values:

Files:

In Windows XP:
  • C:\Documents and Settings\[UserName]\Application Data\[SET OF RANDOM CHARACTERS].exe
In Windows Vista/7:
  • C:\Users\[UserName]\AppData\Roaming\[SET OF RANDOM CHARACTERS].exe
Registry values:
  • HKEY_CURRENT_USER\Software\Microsoft\Windows NT\CurrentVersion\Winlogon "Shell" = "%UserProfile%\Application Data\[SET OF RANDOM CHARACTERS]"
Share this information with other people:

 
//PART 2