Saturday, September 18, 2010

Remove Win64.BIT.Looker.exe (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Win64.BIT.Looker.exe is a false security threat. The real threat is either a rogue program or Trojan horse that displays fake security warnings or notifications about an infection called Win64.BIT.Looker.exe. Recently, this false infection has been displayed alongside a rogue anti-spyware program called Desktop Security 2010. This fake anti-spyware program displays fake Security Center alert that with the following text:
Security Center Alert
To help protect your computer, Security Center has blocked some features of this program
Name: Win64.BIT.Looker.exe
Risk: High
Description: Win64.BIT.Looker software that puts high physical demand on hardware may damage it by excessive wear and tear. This worm can be blocked from firewall and antivirus software.


If you find that your computer is infected with this malware please follow instructions on how to remove Desktop Security 2010. Also, if you have any questions or additional information about this infection, please leave a comment. Good luck and be safe!

Wednesday, September 15, 2010

How to remove IronDefense (Uninstall Instructions)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
IronDefense is a rogue anti-spyware program and visibly a clone of IronDefender. IronDefense comes from fake online anti-malware scanners, misleading or infected web sites. The bad guys also send spam emails with malicious attachments or links to their rogue software and use misleading social engineering methods to distribute malware. Once installed, this fake program will pretend to scan your computer for malicious software and claim to find numerous infected files. It claims that your computer is infected with spyware, adware, dialers, worms and other malware. Finally, it will prompt you to pay for a full version of the program to remove supposedly infected files from your computer. Please don't purchase it. This rogue program won't remove any infections and it won't protect your computer against new threats. If your computer is infected with this fake AV, please follow the removal instructions below to remove IronDefense from your computer.


IronDefense comes bundled with RegistryClever malware and may display pop ups to that lead to flvdirect.com. As a typical fake AV, it will also display fake security warnings and notifications. Iron Defense has its own security center but it looks just like the legitimate Windows Security Center. Obviously, it tries to deceive users into thinking that their computers don't have proper anti-virus software.


And even if you have anti-virus software on your computer, let's say Norton, Kaspersky or Avast the rogue program will still claim that your computer is unprotected. The rogue program costs $49.95, that's definitely a ripoff, you would pay that much for a single anti-spyware program anyway. Furthermore, IronDefense will block task manager and registry editor to evade detection by security products. In some cases it may disable system restore and block nearly all programs on your computer. Not to mention that it will block security software in the first place. It goes without saying that IronDefense is nothing more but a scam. You should call your credit card company and dispute the charges if you have already purchased it. Then please follow IronDefense removal instructions below. Thankfully, this scareware can be removed for free using legitimate anti-malware software mentioned in the removal guide below. Last, but not least, if you have any questions or additional information about this malicious software, please leave a comment. Good luck and be safe online!


IronDefense removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download anti-malware software from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


IronDefense removal instructions in Normal mode:

1. Download Process Explorer iexplore.exe. Double click to open it. Look for IronDefense in the process list and terminate its process(es): F0E84.exe and [RANDOM CHARACTERS].exe.
2. Download  anti-malware software from the list below. Update it and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


IronDefense associated files and registry values:

Files:
In Windows XP:
  • C:\Program Files\FDFCA\F0E84.exe
  • C:\Program Files\FDFCA\Uninstall.exe
  • C:\Documents and Settings\Administrator\Local Settings\Temp\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\[RANDOM CHARACTERS].bin
  • C:\WINDOWS\[RANDOM CHARACTERS].dll
  • C:\WINDOWS\[RANDOM CHARACTERS].cpl
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].bin
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].dll
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].cpl
In Windows Vista & 7:
  • C:\Program Files\FDFCA\F0E84.exe
  • C:\Program Files\FDFCA\Uninstall.exe
  • C:\Users\[User Name]\Local Settings\Temp\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\[RANDOM CHARACTERS].bin
  • C:\WINDOWS\[RANDOM CHARACTERS].dll
  • C:\WINDOWS\[RANDOM CHARACTERS].cpl
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].bin
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].dll
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].cpl
Registry values:
  • HKEY_CURRENT_USER\Software\IronDefense
  • HKEY_LOCAL_MACHINE\software\microsoft\Internet Explorer\ActiveX Compatibility\{188D171F-A126-4A3B-B1DC-ED698FDFCADA}
  • HKEY_LOCAL_MACHINE\software\microsoft\Windows\CurrentVersion\Run "F0E84.exe"
  • HKEY_LOCAL_MACHINE\software\microsoft\Windows\CurrentVersion\Uninstall\IronDefense
  • HKEY_USERS\current\software "C:\Program Files\FDFCA\"
Share this information with other people:

Sunday, September 12, 2010

Remove dating.clicksearch.in (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Dating.clicksearch.in is a browser hijacker that actively promotes the rogue anti-spyware program called IronDefender. It has been distributing other rogue security programs too. Please avoid dating.clicksearch.in and if you somehow ended up on this malicious website, please don't download or install anything from it. Dating.clicksearch.in imitates online anti-malware scanner and claims that your computer is infected with Trojans, worms and other malicious software. If you choose to remove found infections you will end up with a rogue anti-spyware program on your computer. If you find that your computer is infected with IronDefender, please follow IronDefender removal guide. If you've installed other rogue anti-spyware program then you should scan your computer with legitimate and updated anti-malware software. Choose one from the list below. Also, if you have any questions about dating.clicksearch.in or any other rogue security product, please leave a comment. Good luck and be safe online!

Legitimate anti-malware software:
NOTE: before saving the selected program onto your computer, please rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

A screen shot of dating.clicksearch.in


Share this information with other people:

Saturday, September 11, 2010

How to remove RegistryClever (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
RegistryClever is a rogue registry cleaner for Windows that may deliberately give false or exaggerated reports of errors in the registry. The rogue program claims that these errors can result a slowdown of the system, general system instability or even damage your data. Then it claims that in order to avoid serious problems and improve your computer performance, you need to fix the registry. And, of course, RegistryClever will do that for you if you choose to purchase it. In reality, though, it won't fix anything. Registry Clever detects various registry and system errors even on a clean installation of Windows. And that's not because this program is magical. That's because it's a scam. Don't pay for this bogus program and just ignore the false scan results. It goes wihout saying that you should remove RegistryClever from your computer as soon as possible. Please follow the removal instructions below.


RegistryClever is promoted through the use of Ads that lead to the fake software distribution web sites, or though search engine optimized web sites that are designed to rank highly for popular keywords. The rogue program is also promoted through the use of fake online anti-malware scanners or infected web pages. While RegistryClever is running, it will display numerous security alerts about critical errors in the registry, shared DLLs, system services, COM/ActiveX entries and other issues.
84 problems found in 4 sections.
RegistryClever found 84 errors!
Errors in the registry can result in a slowdown of the system, damage to user data and the inability to run the operating system in the future.
Click here for rescan registry and fix errors.

Warning!
Encountered a critical errors in the System Registry!
It is strongly recommended that you fix your System Registry and activate RegistryClever to prevent future damages.

Warning! Errors found may cause
general system instability, system
slowdowns, error messages, or slow
start up time!


RegistryClever order form looks like this:


A screen shot of the main rogue's web page registryclever.com (please don't visit it!)


As you can see, RegistryClever has only one goal - to trick you into purchasing the program. If you have already bought it the please contact your credit card company immediately and dispute the charges. Then please follow RegistryClever removal instructions below. You can remove it either manually or with legitimate anti-malware software listed below. If you have any questions about this malware please leave a comment. Good luck and be safe online!


RegistryClever removal instructions in Normal mode:

1. Download Process Explorer iexplore.exe. Double click to open it. Look for SP Center in the process list and terminate its process(es): RegistryCleverTray.exe and RegistryClever.exe.
2. Download  anti-malware software from the list below. Update it and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


RegistryClever removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download anti-malware software from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


RegistryClever associated files and registry values:

Files:
  • C:\Program Files\RegistryClever Software\RegistryClever\Styles
  • C:\Program Files\RegistryClever Software\RegistryClever\license.txt
  • C:\Program Files\RegistryClever Software\RegistryClever\RegistryClever.exe
  • C:\Program Files\RegistryClever Software\RegistryClever\RegistryCleverTray.exe
  • C:\Program Files\RegistryClever Software\RegistryClever\uninstall.exe
Registry values:
  • HKEY_LOCAL_MACHINE\SOFTWARE\microsoft\DirectDraw\MostRecentApplication "RegistryClever.exe"
  • HKEY_LOCAL_MACHINE\SOFTWARE\microsoft\Windows\CurrentVersion\Uninstall\RegistryClever
  • HKEY_LOCAL_MACHINE\SOFTWARE\RegistryClever
  • HKEY_USERS\current\Software\Microsoft\Windows\CurrentVersion\Run "TrayScan"
  • HKEY_USERS\current\Software\RegistryClever
Share this information with other people:

How to remove IronDefender (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
IronDefender is a rogue security program that masquerades as a legitimate malware removal tool and claims that your computer is infected with worms, dialers, Trojans, spyware and other malicious software. The main goal of this fale software is to deceive you into thinking that your computer is infected with malware. Once installed, IronDefender will pretend to scan your computer for viruses. Then it will give false or exaggerated reports of threats on your computer and state that you should pay for a full version of the program to remove these threats and to proetct your computer against viruses and other security threats. Please don't purchase it and remove IronDefender from the system as soon as possible. If you find that your computer is infected with this malware please follow the removal instructions below.


Iron Defender is promoted mostly through the use of fake online anti-malware scanners. We got the sample of this rogue from the fake online scanner as well. Most of the time this scareware has to be manually installed, but in some cases it might be downlaoded and installed without your knowledge through the use of Trojans downloaders. These Trojans are distributed in various ways, spam e-mails, misleading social engineering schemes, infected web pages or files. While running, IronDefender will display fake security warnings and notifications about critical spyware objects, cyber thieves, password stealing Trojans and other threats.
Spyware Alert!
Your computer is infected with spyware. It could damage your critical files or expose your provate data on the Internet. Click here to register your copy of IronDefender and remove spyware threats from your PC.

Security Center Alert!
Infiltration Alert!
Your computer is being attacked by an Internet virus. It could be a passwrod-stealing attack, a trojan-dropper or similar.
Threat: Crypter-file

733 SPYWARE Found
Attention: DANGER!
IronDefender has detected 733 Critical SPYWARE Objects while scanning the system.


Furthermore, the rogue program will display its Security Center pop-up which impersonates the legitimate Windows Security Center. The fake Security Center will claim that your computer is unprotected against viruses. It will state that you should install an anti-virus software which is IronDefender of course.


If you choose to buy this rogue program it will take you to its billing page. As you can see in the image below, Iron Defender costs $49.95.


The rogue program also displays a pop-up that leads to flvdirect.com (please don't visit this website).


IronDefender is from the same family as ArmorDefender.

Last, but not least, IronDefender may block legitimate anti-spyware and anti-virus programs and disable certain system utilities, task manager, registry editor and system restore. As you can see, it's nothing more but a scam. If you have already bought it then please contact your credit card company and dispute the charges. Finaly, please follow the removal instructions below to remove IronDefender from your computer using legitimate anti-malware software. If you have any questions or addtional information about this misleading program please leave a comment. Good luck and be safe online!


IronDefender removal instructions (in Safe Mode with Networking):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
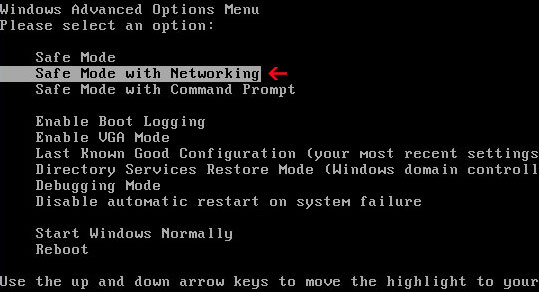

NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download anti-malware software from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


IronDefender removal instructions in Normal mode:

1. Download Process Explorer iexplore.exe. Double click to open it. Look for IronDefender in the process list and terminate its process(es): F0E84.exe and gen4436.exe.
2. Download  anti-malware software from the list below. Update it and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
3. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


IronDefender associated files and registry values:

Files:
In Windows XP:
  • C:\Program Files\FDFCA\F0E84.exe
  • C:\Program Files\FDFCA\Uninstall.exe
  • C:\Documents and Settings\Administrator\Local Settings\Temp\gen4436.exe
  • C:\WINDOWS\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\[RANDOM CHARACTERS].bin
  • C:\WINDOWS\[RANDOM CHARACTERS].dll
  • C:\WINDOWS\[RANDOM CHARACTERS].cpl
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].bin
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].dll
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].cpl
In Windows Vista & 7:
  • C:\Program Files\FDFCA\F0E84.exe
  • C:\Program Files\FDFCA\Uninstall.exe
  • C:\Users\[User Name]\Local Settings\Temp\gen4436.exe
  • C:\WINDOWS\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\[RANDOM CHARACTERS].bin
  • C:\WINDOWS\[RANDOM CHARACTERS].dll
  • C:\WINDOWS\[RANDOM CHARACTERS].cpl
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].exe
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].bin
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].dll
  • C:\WINDOWS\system32\[RANDOM CHARACTERS].cpl
Registry values:
  • HKEY_CURRENT_USER\Software\IronDefender
  • HKEY_LOCAL_MACHINE\software\microsoft\Internet Explorer\ActiveX Compatibility\{188D171F-A126-4A3B-B1DC-ED698FDFCADA}
  • HKEY_LOCAL_MACHINE\software\microsoft\Windows\CurrentVersion\Run "F0E84.exe"
  • HKEY_LOCAL_MACHINE\software\microsoft\Windows\CurrentVersion\Uninstall\IronDefender
  • HKEY_USERS\current\software "C:\Program Files\FDFCA\"
Share this information with other people:

 
//PART 2