Saturday, August 7, 2010

How to remove Wireshark Antivirus (Uninstall Instructions)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Wireshark Antivirus is a fake anti-virus program. It reports false system security threats on the computer. The main goal of this rogue program is to make you think that your computer is infected with all sorts of malware. Wireshark Antivirus then prompts to pay for a full version of the program to remove the threats. Don't purchase it! If you have already bought this rogue program then please contact your credit card company as soon as possible and dispute the charges. WiresharkAntivirus flags Windows OS (or other harmless) files as malware. It's obvious that legitimate anti-virus or anti-spyware programs don't do that. Do not delete those files because otherwise Windows OS may not operate properly. Instead, please remove Wireshark Antivirus from your computer as soon as possible. This can be done either manually or with anti-malware programs. Of course, we recommend using anti-malware programs because the rogue program may come bunlded with other viruses that you may not be able to remove manually. Please follow the removal instructions below.


Wireshark Antivirus is from the same family as XJR Antivirus, AKM Antivirus 2010 Pro and Your PC Protector. Please note that this rogue program has nothing to do with Wireshark which is a very helpful packet analyzer made by CACE Technologies Inc. They made a public announcement about this issue. It's not the first time when rogue programs abuses reputable software names.

Once Wireshark Antivirus is installed, it will pretend to scan your computer and display a list of infected files that can be cleaned or removed only with a full version of the program. This is nothing more but a scam. The worst thing is that this fake program blocks legitimate anti-malware software and security related websites. It may even display adult icons on your Desktop and redirect you to various misleading websites. It will block Task Manager, registry editor and other useful tools too. Furthermore, it will constantly display fake security alerts and pop ups about non-existent infections or system security threats. If you attempt to run a program (let's say Notepad) Wireshark Antivirus blocks it and display the following warning:
Warning!
Running of application is impossible.
The file C:\Windows\System32\notepad.exe is infected.
Please activate your antivirus program.


Some of the other fake alerts you may see on your computer screen:


Wireshark Antivirus is one of those very annoying rogue security products. It uses various misleading methods to trick you into purchasing the program. Besides, it's promoted through the use of Trojans and other malware. It's a virus itself. If your computer got infected with this rogue program please follow the removal instructions below to remove Wireshark Antivirus for free using legitimate anti-malware programs. You should also purge all system restore points and make a new one after you successfully remove this virus from your PC. Last, but not least, if you have any additional information or questions about this malware please leave a comment. Good luck and be safe!

UPDATE: you may use this key: significantother to activate the rogue program and make the removal procces a bit easier. Many thanks to S!Ri.URZ.


Wireshark Antivirus removal instructions:

1. Go to Start->Run or press WinKey+R. Type in "command" and press Enter key.


2. In the command prompt window type "notepad". Notepad will come up.


3. Copy all the text in blue color below and paste into Notepad.

Windows Registry Editor Version 5.00
[HKEY_CLASSES_ROOT\exefile\shell\open\command]
@="\"%1\" %*"

4. Save file as regfix.reg to your Desktop. NOTE: (Save as type: All files)


5. Double-click on regfix.reg file to run it. Click "Yes" for Registry Editor prompt window. Then click OK.
6. Download one of the following anti-malware applications:
NOTE: before saving the selected program onto your computer, please rename the installer to iexplore.exe or winlogon.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
7. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Wireshark Antivirus associated files and registry values:

Files:
  • C:\Program Files\adc_w32.dll
  • C:\Program Files\alggui.exe
  • C:\Program Files\nuar.old
  • C:\Program Files\skynet.dat
  • C:\Program Files\svchost.exe
  • C:\Program Files\wp3.dat
  • C:\Program Files\wp4.dat
  • C:\Program Files\wpp.exe
  • C:\Program Files\Wireshark Antivirus\
  • C:\Program Files\Wireshark Antivirus\Wireshark Antivirus.exe
  • %UserProfile%\Local Settings\Temp\win1.tmp
  • %UserProfile%\Local Settings\Temp\win2.tmp
  • %UserProfile%\Start Menu\Programs\Wireshark Antivirus\
Registry values:
  • HKEY_CURRENT_USER\Software\Wireshark Antivirus
  • HKEY_CLASSES_ROOT\CLSID\{149256D5-E103-4523-BB43-2CFB066839D6}
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\Browser Helper Objects\{149256D5-E103-4523-BB43-2CFB066839D6}
  • HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Services\AdbUpd
Share this information with other people:

Friday, August 6, 2010

My Security Shield removal instructions (Uninstall Guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
My Security Shield is a piece of malware that pretends to be a legitimate anti-virus software. Actually, it's pretty generic looking rogue anti-virus program that may arrive on the compromised computer as a manually install or may be downloaded by other malware. Usually, My Security Shield is promoted through the use of fake online scanners and infected websites. It prevents other applications from being executed and displays fake security warnings. MySecurityShield reports false scan results and states that your computer is infected with various viruses, adware, spyware or other malware. As a typical rogue anti-virus program it will prompt you to pay for a full version of the program to remove the infections. It goes without saying that you should uninstall this virus from your computer instead of buying it. Unfortunately, it's rather difficult to remove this fake program from a computer, thankfully we've got My Security Shield removal instructions to help you. Please follow the removal instructions below.


While the rogue program is running, it will flag harmless files as malware infections. In fact, My Security Shield drops several files on the system and later detects those files Trojans, worms or other malicious software. This misleading application adds itself to the list of programs that start automatically when Windows OS starts. It will hijack Internet Explorer and other web browsers. It may display search results from findgala.com instead of Google. And of course, it may block safe security related websites and legitimate anti-virus and anti-spyware programs. Last, but not least, you wouldn't imagine a rogue program without fake security alerts and pop-ups from Windows taskbar. My Security Shield has it all. The fake program may display any of the following warning messages:
Warning! Virus detected
Threat Detected: Trojan-PSW.VBS.Half
Description: This is a VBScript-virus. It steals user's passwords.


The home page of My Security Shield is www5.my-security-shield.com. Please do not visit this site.


My Security Shield is from the same family as Security Master AV and My Security Engine scareware.

Also note that this rogue program may come bundled with other malware. Although, it can be removed manually, but we strongly recommend you to use an anti-virus or anti-spyware program in order to remove My Security Shield completely from your computer. Read full removal details below. If you have already bought the rogue program, please contact your credit card company and dispute the charges. If you have any questions or additional information about this malware please leave a comment. Good luck and be safe!


My Security Shield removal instructions:

1. Download recommended anti-malware software (Spyware Doctor) and run a full system scan to remove this virus from your computer.

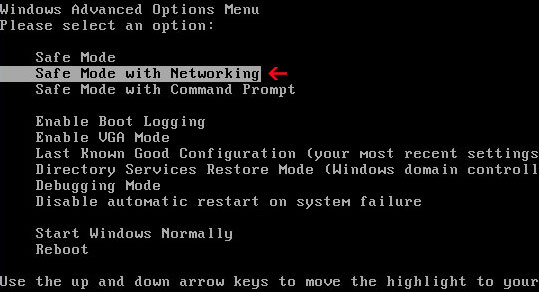
If you can't download it, please reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Open Internet Explorer and download STOPzilla. Once finished, go back into Normal Mode and run it. That's It!


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.


My Security Shield associated files and registry values:

Files:
  • C:\Documents and Settings\All Users\Application Data\345d567\
  • C:\Documents and Settings\All Users\Application Data\345d567\4475.mof
  • C:\Documents and Settings\All Users\Application Data\345d567\mozcrt19.dll
  • C:\Documents and Settings\All Users\Application Data\345d567\MS345d_2129.exe
  • C:\Documents and Settings\All Users\Application Data\345d567\MSS.ico
  • C:\Documents and Settings\All Users\Application Data\345d567\sqlite3.dll
  • C:\Documents and Settings\All Users\Application Data\345d567\MSSSys\vd952342.bd
  • C:\Documents and Settings\All Users\Application Data\MSHBXRCOBWS\
  • C:\Documents and Settings\All Users\Application Data\MSHBXRCOBWS\MSJYQMS.cfg
  • %UserProfile%\Application Data\My Security Shield\
  • %UserProfile%\Application Data\My Security Shield\cookies.sqlite
  • %UserProfile%\Application Data\My Security Shield\Instructions.ini
  • %UserProfile%\Recent\cid.drv
  • %UserProfile%\Recent\CLSV.tmp
  • %UserProfile%\Recent\DBOLE.exe
  • %UserProfile%\Recent\delfile.sys
  • %UserProfile%\Recent\fan.dll
  • %UserProfile%\Recent\grid.sys
  • %UserProfile%\Recent\kernel32.exe
  • %UserProfile%\Recent\kernel32.sys
  • %UserProfile%\Recent\PE.dll
  • %UserProfile%\Recent\PE.tmp
  • %UserProfile%\Recent\runddlkey.drv
  • %UserProfile%\Recent\SICKBOY.drv
  • %UserProfile%\Recent\std.dll
  • %UserProfile%\Recent\tempdoc.tmp
  • %UserProfile%\Recent\tjd.sys
Registry values:
  • HKEY_CURRENT_USER\Software\3
  • HKEY_CLASSES_ROOT\CLSID\{3F2BBC05-40DF-11D2-9455-00104BC936FF}
  • HKEY_CLASSES_ROOT\MS345d_2129.DocHostUIHandler
  • HKEY_USERS\.DEFAULT\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=2129&q={searchTerms}"
  • HKEY_CURRENT_USER\Software\Classes\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=2129&q={searchTerms}"
  • HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer "PRS" = "http://127.0.0.1:27777/?inj=%ORIGINAL%"
  • HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "RunInvalidSignatures" = "1"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\User Agent\Post Platform "control/7.02129"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "My Security Shield"
  • HKEY_CLASSES_ROOT\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=2129&q={searchTerms}"
  • HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "CheckExeSignatures" = "no"
Share this information with other people:

Tuesday, August 3, 2010

How to remove Antivirus (AnVi) malware (Uninstall Instructions)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Here's another rogue program with an original name: Antivirus. Actually, it's from the same family as Protection Center, Data Protection and Digital Protection scareware. The rogue program is installed through the use of Trojan Horses and other malware that come from shady or infected websites or through software vulnerabilities. You can use Secunia Online Software Inspector to make sure that your PC has a minimum security baseline against known patched vulnerabilities. Once installed, Antivirus will state that your computer has been infected with Trojans, adware, spyware, worms, tracking cookies and other malicious software. Then it will prompt you to pay for a full version of the program to remove the infections. Don't buy it! Instead, please follow the removal instructions below to remove Antivirus from your computer for free either manually or with legitimate anti-malware software.


Antivirus (AnVi) video (thanks to rogueamp):


While Antivirus is running it will attempt to uninstall your anti-virus or anti-spyware program from the system. It will also block all the other legitimate anti-malware programs and security websites. The rogue program does this in order to protect itself from being removed. What is more, Antivirus (AnVi) may come bundled with TDSS rootkit which usually redirects Google searc results to entirely unrelated websites. Most of the time, those website promote rogue products or provide false information, spam and etc. And of course, you wouldn't imagine a rogue anti-spyware program without a bunch of fake security warnings a pop-ups claiming that your computer is seriously infected or under attack from a remote computer. The text of some fake security alerts are:

"Warning! Virus threat detected!
Virus activity detected!
Net-Worm.Win32 has been detected. This adware module advertises websites with explicit content. Be advised of such content being possibly illegal. Please click the button below to locate and remove this threat."


It goes without saying that should uninstall Antivirus from your computer as soon as possible. If you have already purchased it then you should contact your credit card company immediately and dispute the charges. Then please follow free Antivirus removal instructions below. If you have a redirect virus alongside this rogue program, please use free TDSSKiller utility from Kaspersky lab. Also, your comments are more than welcome. Good luck and be safe!


Antivirus removal instructions (in Safe Mode with Networking, Method 1):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.

2. Download SUPERAntispyware, MalwareBytes Anti-malware, Spybot - Search & Destroy or Spyware Doctor and run a full system scan. NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning. Then reboot your computer in "Normal Mode" and run  a system scan again. That's it!
4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Antivirus removal instructions: (Method 2)

1. Download TDSSKiller.exe from Kaspersky website.
2. Execute the file TDSSKiller.exe (NOTE: you may have to rename TDSSKiller.exe to explorer.com yourself or download already renamed explorer.com file in order to run it)
3. Follow the prompts and wait for the scan and disinfection process to be over.
More detailed TDSSKiller tutorial: http://support.kaspersky.com/viruses/solutions?qid=208280684
4. Download one of the following anti-malware software and run a full system scan:
5. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.


Antivirus associated files and registry values:

Files:
  • C:\Program Files\AnVi\about.ico
  • C:\Program Files\AnVi\activate.ico
  • C:\Program Files\AnVi\avt.db
  • C:\Program Files\AnVi\avt.exe
  • C:\Program Files\AnVi\avtext.dll
  • C:\Program Files\AnVi\avthook.dll
  • C:\Program Files\AnVi\buy.ico
  • C:\Program Files\AnVi\help.ico
  • C:\Program Files\AnVi\scan.ico
  • C:\Program Files\AnVi\settings.ico
  • C:\Program Files\AnVi\splash.mp3
  • C:\Program Files\AnVi\Uninstall.exe
  • C:\Program Files\AnVi\update.ico
  • C:\Program Files\AnVi\virus.mp3
Registry:
  • HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run\Antivirus
  • HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies \System\DisableTaskMgr
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies \System\DisableTaskMgr
Please share this information with other people:

Sunday, August 1, 2010

Remove av-fox.com and antivirfox.com (Free Removal Instructions)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
There are large amounts of websites on the Internet right now advertising a rogue anti-virus program called Antivir Solution Pro or just Antivir Solution. Typically, there are browser hijackers that claim that your computer has been infected with spyware. Such websites "pushes" rogue anti-virus programs and Antivir Solution Pro is at the top of the list. And obviously, there are also fake purchase pages. This time we have another four websites that look all the same and promote Antivir Solution Pro scareware:

  • av-fox.com
  • av-fox.net
  • antivirfox.com
  • antivirfox.net

The above websites provide false information and recommend buying rogue anti-virus software. If your computer is infected with Antivir Solution Pro then I guess you have already seen such bogus websites. Usually, users of compromised computers are redirected to a pay page of Antivir Solution Pro, but there is also a fake page titled "Internet Explorer Warning - visiting this web site may harm your computer!". If you find that your computer is infected with Antivir Solution Pro malware ir you are beinf redirected to av-fox.com, av-fox.net, antivirfox.com or antivirfox.net then please follow Antivir Solution Pro removal instructions. If you have already purhcased the bogus program then you should contact your credit card company and dispute the charges. As always, good luch and be safe!

Screenshot of av-fox.com


Share this information with other people:

Remove "Attention! Your web page request has been cancelled." (Free Removal)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
"Attention! Your web page request has been cancelled." is a fake security warning. It looks just like the legitimate safe browsing warning which you probably have seen if you use Mozilla Firefox.

Fake "Attention! Your web page request has been cancelled." warning:


Legitimate "Reported Attack Site" warning:


The fake one pushes rogue anti-virus programs. If you click the "Fix Now" button you will be prompted to download or install a fake anti-virus program. The legitimate one doesn't promote any security software at all. It simply states that the website you're about to visit is currently listed as suspicious. Please note the differences between these two security warnings. If you see the Attention! Your web page request has been cancelled. warning, be sure that it's a fake one and that your computer is infected with some sort of malware, most likely Trojan Horse. Thankfully, there are some free anti-malware applications that you may use to remove malware. You should scan your PC with at least two anti-malware programs from the list below. Good luck and be safe!

Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.

Share this information with other people:

 
//PART 2