Antispybase.com is a misleading websites which promotes AV Security Suite scareware. It's one of the most active AV Security Suite related websites at the moment. The rogue anti-spyware programs blocks nearly all legit websites and redirects users of compromised computers to Antispybase.com. Some people think that Antispybase.com is a browser hijacker and that they have an adware on their computer. In reality, they got infected with AV Security Suite malware and couple of other Trojans. Those Trojans hijacks web browsers and search results.
If you are being constantly redirected to Antispybase.com, then you should follow AV Security Suite removal instructions as soon as possible. Thankfully, you can remove Antispybase.com and related malware from your computer for free using legitimate anti-malware software. Full details on how to remove this virus from your computer on the link above. If you have any questions or additional information about this infection, please don't hesitate and leave a comment. Good luck and be safe!
As you may already know, rogue/fake anti-virus programs are promoted and installed mostly through the use of Trojan viruses. There are many fake or infected websites on the Internet. Those websites are the main source of infection. One of such websites is www2(dot)braveguard5(dot)co(dot)cc (please don't visit it!). I took this particular websites as an example, because it displays fake online video player and states that "Video ActiveX Object Error: Your browser cannot display this video file."
Apparently, this fake Video ActiveX Object Error message was made for Windows Vista users, but works for Windows XP users too. This is the first visual sign that ActiveX Object Error warning is fake, because you can't actually expect Windows Vista style pop-up on your Windows XP machine. Once you click "Continue", you will be prompted to download .exe file which supposedly fixes this error. However, in reality, you will get a Trojan Horse instead of working player. This is a very common way how Internet users infect their computers. Remember, if you have Flash player installed on your computer then you don't need any other. Flash player can be downloaded from the Adobe website. Also, if you get a pop-up telling you to update your flash player, please make sure that it's from Adobe.
Finally, if you unadvisedly installed a fake flash player on your PC then you should scan your computer with an anti-malware program. You can choose one from the list below. All these programs are free.
AV Security Suite is yet another fake anti-virus program which reports false system security threats, redirects browsers, disables legitimate security software, Task Manager and other tools to make you think that your computer is infected with malicious software. AVSecuritySuite is basically a rename of Antispyware Soft and Antivirus Suite. This fake antivirus program will compromise your PC security. It will state that your computer is infected with spyware, adware and other viruses as well. And of course, as a typical rogue program, it will prompt you to pay for a full version of the program to remove the infections and to make your computer protected against hacker attacks, identity theft and new types of malware. Thankfully, you can remove AV Security Suite from your computer for free using legitimate anti-malware programs and additional security tools. If you find that your computer is infected with this bogus program please follow the removal instructions below.
Usually, AV Security Suite scareware is installed after visiting an infected site which installs a Trojan Downloader. It later downloads the rogue program on the computer. Once installed, this fake antivirus program will report numerous false system security threats, display fake warnings and pop-ups, redirect searches, disable Task Manager and block legit anti-malware or anti-virus programs. It will even impersonate Windows Security Center and state that you should activate AV Security Suite to protect your computer against malware. Besides, it may block all programs, not only security software. For example, it may block Notepad and claim that it's infected. The fake warning reads:
"Windows Security alert Application cannot be executed. The file notepad.exe is infected. Do you want to active your antivirus software now?"
Another problem is that this virus configures Windows to use a proxy server. That's why you will probably see a fake warning about insecure connection or a misleading website instead of requested one. It will block security related websites in the first place and display the following text:
"This website has been reported as unsafe We recommend that you do not continue to this website. This website has been reported to Microsoft for containing threats to your computer that might reveal personal or financial information."
And of course, you will get the usual round of pop-ups and fake security warnings claiming that your computer is infected with malware or under attack from a remote computer.
"Windows Security alert Windows reports that computer is infected. Antivirus software helps to protect your computer against viruses and other security threats. Click here for the scan your computer. Your system might be at risk now."
"Antivirus software alert Infiltration Alert Your computer is being attacked by an internet virus. It could be a password-stealing attack, a trojan-dropper or similar."
As you can see, AV Security Suite is absolutely needless and potentially harmful program. In order to completely remove this virus from your computer you need to use legitimate anti-malware software. Most importantly, don't buy it! If you have already purchased this rogue program then please contact your credit card company and dispute the charges. If you have any questions or additional information about this virus, please don't hesitate and leave a comment.
AV Security Suite removal instructions (in Safe Mode with Networking):
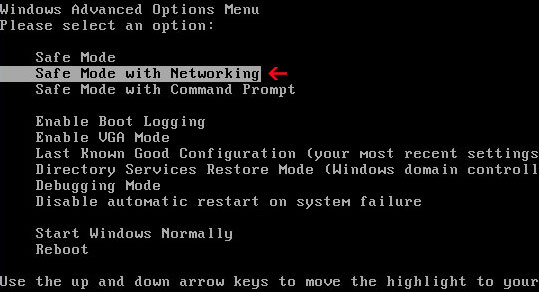
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
NOTE:Login as the same user you were previously logged in with in the normal Windows mode.
2. Launch Internet Explorer. In Internet Explorer go to: Tools->Internet Options->Connections tab. Click Lan Settings button and uncheck the checkbox labeled Use a proxy server for your LAN. Click OK.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe.With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Alternative AV Security Suite removal instructions using HijackThis (in Normal mode):
1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro). Launch the iexplore.exe and click "Do a system scan only" button. If you can't open iexplore.exe file then download explorer.scr and run it.
2. Search for similar entries in the scan results: R1 – HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=127.0.0.1 O4 – HKLM\..\Run: [utrfklpe] C:\Documents and Settings\[User]\Local settings\Application data\oprtklr\andqgs.exe O4 – HKCU\..\Run: [utrfklpe] C:\Documents and Settings\[User]\Local settings\Application data\oprtklr\andqgs.exe
The process name will be different in your case [RANDOM].exe, located in C:\Documents and Settings\[User]\Local settings\Application data\ Select all similar entries and click once on the "Fix checked" button. Close HijackThis tool.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe.With all of these tools, if running Windows 7 or Vista they MUST be run as administrator. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
AV Security Suite associated files and registry values:
Protection Center is a fake antivirus program that gives false reports of threats on the computer. This misleading program claims that your computer is infected with malicious software. It constantly displays fake security warnings and prompts you to pay for a full version of the program to remove the infections which actually don't even exist. ProtectionCenter flags absolutely harmless files as malware. Please don't manually remove any of those files because some of them may actually be Windows system files. If you find that your computer is infected with this virus, please follow the removal instructions below. The good news is that you can remove Protection Center from your computer for free using free anti-malware programs.
Most people are curious how they got infected with Protection Center? Usually, this rogue program has to be manually installed. Most of the time ProtectionCenter pretends to be flash player or an update or any other legitimate software. Of course, it may come bundled with other malware or enter your computer without your consent through software vulnerabilities. One way or another, Protection Center should be removed from the system as soon as possible.
While running, the rogue program displays numerous fake security alerts and pop-ups. Some of those alerts read:
"Warning! Virus threat detected! Virus activity detected! Email-Worm.BAT adware has been detected. This adware module advertises websites with explicit content. Be advised of such content being possibly illegal. Please click the button below to locate and remove this threat now."
"Danger! A security threat detected on your computer. This malicious program may steal your private data. Click on the message to ensure the protection of your computer."
However, the biggest problem is that Protection Center may block Task Manager and legitimate anti-virus and anti-malware software. It some cases it blocks all executable files. Besides, this rogue program can come bundled with TDSS rootkit. That's why we strongly recommend you to scan your computer with at least one legitimate anti-malware program provided in the removal instructions below and run a system scan with free TDSS rootkit removal utility called TDSSKiller. Please note that you may have to reboot your computer is Safe Mode with Networking in order to download recommend removal tools. Just follow Protection Center removal instructions below. By the way, if you have already purchased it, then contact your credit card company and dispute the charges. If you have any questions or additional information about this malware, please leave a comment. Good luck and be safe!
Protection Center removal instructions (in Safe Mode with Networking, Method 1):
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
NOTE:Login as the same user you were previously logged in with in the normal Windows mode.
2. Download one of the following anti-malware software and run a system scan:
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning. Then reboot your computer in "Normal Mode" and run a system scan again. That's it! 4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Protection Center removal instructions: (Method 2)
1. Go to Start->Run or press WinKey+R. Type in "command" and press Enter key.
2. In the command prompt window type "notepad". Notepad will come up.
3. Copy all the text in blue color below and paste into Notepad.
Windows Registry Editor Version 5.00 [HKEY_CLASSES_ROOT\exefile\shell\open\command] @="\"%1\" %*"
4. Save file as regfix.reg to your Desktop. NOTE: (Save as type: All files) 5. Double-click on regfix.reg file to run it. Click "Yes" for Registry Editor prompt window. Then click OK. 6. Download and execute TDSSKiller.exe (NOTE: you may have to rename TDSSKiller.exe to explorer.com yourself or download already renamed explorer.com file in order to run it) 3. Follow the prompts and wait for the scan and disinfection process to be over. Close all programs and press “Y” key to restart your computer. More detail TDSSKiller tutorial: http://support.kaspersky.com/viruses/solutions?qid=208280684 4. Download one of the following anti-malware software and run a system scan:
Security Master AV is a fake anti-virus program that uses misleading methods to make you think that your computer is infected with malicious software. First, it displays fake security warnings and claims that malicious software has been detected on your computer. Then, it runs a fake system scan and displays a list of infected files. Of course, the scan results are false. Security Master AV flags harmless files as malware. It may also list Windows system files in its scan report, so don't manually delete any of those files. Finally, the rogue program will prompt you to pay for a full version of the program to remove the infections. It goes without saying that you shouldn't purchase it. Instead, please remove Security Master AV from your computer as soon as possible using the removal instructions below.
You may ask, where did it come from? Usually, such bogus programs come from fake online scanners and fake video websites sites or you may simply click an infected advertisement. Security Master AV can come bundled with other malware, but this is less common situation. By the way, the rogue program has to be manually installed, but the problem is that it pretends to be a legitimate program, that's why some users don't understand that it's actually a Trojan or other malware. Once installed, Security Master AV will display fake security alerts. Some of those alerts or pop-ups read:
"System alert Potentially harmful programs have been detected in your system and need to be dealt with immediately. Click here to remove them using Security Master AV."
"System alert Suspicious software which may be malicious has been detected on your PC. Click here to remove this threat immediately using Security Master AV."
Furthermore, this fake program hijacks Internet Explorer and changes default search engine to findgala.com. It blocks security related websites, modifies Windows Hosts file and blocks legitimate anti-malware programs. Thankfully, we've got remove instructions to help you. It's possible to remove Security Master AV manually, but we strongly recommend you to scan your PC with reputable and legitimate anti-malware software. Please follow the removal instructions below. And by the way, if you have already purchased SecurityMasterAV, then you should contact your credit card company and dispute the charges. Also, if you have any questions or additional information about this virus, please leave a comment. Good luck and be safe!
Security Master AV removal instructions using HijackThis (in Normal mode):
1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro). Launch the iexplore.exe and click "Do a system scan only" button. If you can't open iexplore.exe file then download explorer.scr and run it.
2. Search for similar entries in the scan results: O4 - HKCU\..\Run: [Security Master AV] "C:\Documents and Settings\All Users\Application Data\345d567\SM345d.exe" /s /d Select all similar entries and click once on the "Fix checked" button. Close HijackThis tool.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
Security Master AV removal instructions (in Safe Mode with Networking):
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
NOTE:Login as the same user you were previously logged in with in the normal Windows mode.
3. Download at least one anti-malware program from the list below and run a full system scan.
NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning. 4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Security Master AV associated files and registry values:
Files:
C:\Documents and Settings\All Users\Application Data\345d567\
C:\Documents and Settings\All Users\Application Data\345d567\16.mof
C:\Documents and Settings\All Users\Application Data\345d567\mozcrt19.dll
C:\Documents and Settings\All Users\Application Data\345d567\SM345d.exe
C:\Documents and Settings\All Users\Application Data\345d567\SMAV.ico
C:\Documents and Settings\All Users\Application Data\345d567\sqlite3.dll
C:\Documents and Settings\All Users\Application Data\345d567\Quarantine Items\
C:\Documents and Settings\All Users\Application Data\345d567\SMAVSys\
C:\Documents and Settings\All Users\Application Data\345d567\SMAVSys\vd952342.bd
C:\Documents and Settings\All Users\Application Data\SMNPCTCAV\