Avtivirus-fortress.com is a misleading web site that promotes the rogue anti-virus program called Antivirus Suite. It doesn't host harmful files at the moment (of course that might change at any time), but it provides false information and misleads users into purchasing the rogue program. There are many fake reviews and feedback from people all around the world on avtivirus-fortress.com web site. And it also stands for a pay page of Antivirus Suite. It goes without saying that you should avoid Avtivirus-fortress.com.
If you are being constantly redirected to avtivirus-fortress.com then this means that your computer is already infected with Antivirus Suite malware. Thankfully, this infection can be removed from a computer entirely for free using legitimate anti-malware programs. Please follow Antivirus Suite removal instructions and remove this annoying virus from your PC as soon as possible. If you have any questions or additional information about this infection, don't hesitate and leave a comment. Good luck and be safe!
"Your Protection" is a fake anti-virus program and it's a clone of User Protection malware. Needless to say, that this fake program should be removed from your computer immediately. If you are reading this article, then your computer is probably infected with Your Protection virus.
So, what is it and how to remove this infection? Basically, it's a trojan virus that pretends to be legitimate antivirus software. The rogue program comes mostly from fake online anti-malware scanners, compromised web sites, or through software vulnerabilities (web browser, pdf and etc). Once installed, it displays fake warnings, pop-ups and reports false system security threats to make you think that your PC is infected with malicious software, whereas the only real infection is YourProtection. Thankfully, we've got instructions to help you.
Just like it's predecessors, Your Protection attempts to uninstall legitimate anti-virus anti-spyware programs from from your computer. It scans computer for the following antivirus programs: avast!, AVG, Avita AntiVir, NOD32, F-Secure and others. The rogue program states that found anti-virus program is infected and that you need to uninstall it. That's of course not true.
When running, this scareware also displays many fake security warnings. Some of them will state:
"User's activity loggers detected! It's strongly recommended to remove detected threats right now!"
"Zlob.Porn.Ad adware has been detected. This adware module advertises websites with explicit content. Be advised of such content being possibly illegal. Please click the button below to locate and remove this threat now."
"Danger! A security threat detected on your computer. TrojanASPX.JS.Win32. It strongly recommended to remove this threat right now. Click on the message to remove it."
Of course, you will probably see more of these fake alerts on your computer screen. Also, you may find several porn icons on your Desktop. That's a part of this infection. Those shortcuts redirects user to porn web sites or other infected web sites, so don't click on them.
As you probably know, Your Protection reports fake infections to scare you into purchasing the bogus program. Don't do that. This is nothing more but a scam. However, if you have already purchased it, then you should contact your credit card company as soon as possible and dispute the charges.
Last, but not least, YourProtection may come bundled with TDSS rootkit. This rookit usually hijacks Internet Explorer (other web browsers too) and redirects users to entirely unrelated web sites. Very often those web sites are harmful or full of false information. It's very important to remove TDSS infection. That's why you should follow the removal instructions below very carefully and use suggested malware removal tools. Your Protection virus can be removed manually, but because of possible TDSS infection manual removal is not recommended. If you have any questions about this virus or any information that might help to remove it, don't hesitate and leave a comment. Good luck and be safe!
Your Protection removal instructions:
1. Download the file TDSSKiller.zip and extract it into a folder 2. Execute the file TDSSKiller.exe (NOTE: you may have to rename TDSSKiller.exe to explorer.com yourself or download already renamed explorer.com file in order to run it) 3. Follow the prompts and wait for the scan and disinfection process to be over. Close all programs and press “Y” key to restart your computer. More detail TDSSKiller tutorial: http://support.kaspersky.com/viruses/solutions?qid=208280684 4. Download one of the following anti-malware software and run a full system scan:
5. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security. User Protection associated files and registry values:
Files:
C:\Program Files\Your Protection
C:\Program Files\Your Protection\Uninstall.exe
C:\Program Files\Your Protection\urp.db
C:\Program Files\Your Protection\urpext.dll
C:\Program Files\Your Protection\urphook.dll
C:\Program Files\Your Protection\urpprot.exe
C:\Documents and Settings\All Users\Application Data\kjrofjkrtm.dll
Protectedlife.net is a misleading web site that promotes the rogue anti-virus program called Antivirus Suite. It seems like this web template (see image below) works quite well because it's being used for a while now. Widely spread malware Antivirus Soft redirects infected users to bogus web sites that look just like Protectedlife.net. Read Remove Av-2010.com scam article for more information.
As for Protectedlife.net, that web site isn't harmful, but it provides clearly false information. Antivirus Suite is not a legitimate program. It's a scam. And you shouldn't purchase it. Otherwise you will simply lose your money. By the way, if you have already purchased Antivirus Suite malware, then you should contact your credit card company and dispute the charges. If you are being constantly being redirected to Protectedlife.net then this is a sign that your computer is infected with Antivirus Suite. In order to remove this virus from your computer please read this article: Antivirus Suite removal instructions. Good luck and be safe!
"INFILTRATION ALERT" Win32/Nuqel.E is a false system security threat commonly reported by rogue antivirus programs. Recently this fake warning is being used by the rogue anti-virus program called Antivirus Suite. The fake warning reads:
"Antivirus software alert INFILTRATION ALERT Your computer is being attacked by an internet virus. It could be a password-stealing attack, a trojan - dropper or similar. Threat: Win32/Nuqel.E"
If you see this or similar alerts on your computer screen then you are infected with malware. Please follow the Antivirus Suite removal instructions. NOTE: such alert might be used by other rogue programs. Good luck and be safe!
Antivirus Suite is malware classified as a rogue anti-virus program. It is one of many fake antivirus applications that display fake security warnings or pop-ups from the Windows taskbar and report false threats to make you think that your computer is infected with malicious software. It then prompts you to pay for a full version of the program to remove the infections which don't even exist. If you are reading this article then your computer is probably infected with this virus. Thankfully, we've got the instructions to help.
How to remove Antivirus Soft/Antivirus Suite video: (thanks to rogueamp)
This fake program is a clone of Antivirus Soft malware and it uses basically the same "self-protection" methods as its predecessor. It blocks legitimate programs and displays fake warning titled "Application cannot be executed".
Some other fake alerts read: "Windows Security alert Windows reports that computer is infected. Antivirus software helps to protect your computer against viruses and other security threats. Click here for the scan you computer. Your system might be at risk now."
"Antivirus software alert Infiltration Alert Your computer is being attacked by an internet virus. It could be a password-stealing attack, a trojan - dropper or similar."
The bad news is that Antivirus Suite hijacks Internet Explorer and configures Windows Internet settings to use a proxy server. The proxy server blocks nearly all web sites, especially security related ones and displays this fake warning titled "Internet Explorer Warning - visiting this web site may harm your computer!".
When you attempt to open other programs, AntivirusSuite will state that they are infected and finally will prompt you to pay for a full version of the program to remove the infections that cause Windows OS problems/errors. Of course, this is nothing more but a scam. Don't buy this bogus software.
Screenshot of Protectedlife.net
Antivirus Suite is absolutely needless software. In some cases it can be even dangerous (if it comes bundled with other malware). It goes without saying that you should remove this virus from your computer as soon as possible. Please follow the removal instructions below. Those are the steps that normally work. However, note that in some cases Antivirus Suite may block Safe Mode with Networking or even prevent you from doing anything at all. In such case, you will have to download the files requested in this guide on another computer and transfer them to the infected computer using USB flash drive or any other external drive. If you have any questions or any related information, don't hesitate and leave a comment. Good luck and be safe!
Antivirus Suite removal instructions (in Safe Mode with Networking):
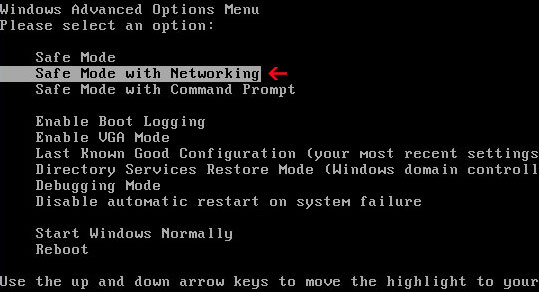
1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
NOTE:Login as the same user you were previously logged in with in the normal Windows mode.
2. Launch Internet Explorer. In Internet Explorer go to: Tools->Internet Options->Connections tab. Click Lan Settings button and uncheck the checkbox labeled Use a proxy server for your LAN. Click OK.
3. Download SUPERAntispyware, MalwareBytes Anti-malware or Spybot - Search & Destroy and run a full system scan.NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning. Then reboot your computer in "Normal Mode" and run a system scan again. That's it! 4. New threats appear every day. In order to protect your PC from such (new) infections we strongly recommend you to use ESET Smart Security.
Alternative Antivirus Suite removal instructions using HijackThis (in Normal mode):
1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro). Launch the iexplore.exe and click "Do a system scan only" button. If you can't open iexplore.exe file then download explorer.scr and run it.
2. Search for similar entries in the scan results: O4 – HKCU\..\Run: [wdpayrmq] C:\Documents and Settings\User\Local Settings\Application Data\krtopldrf\woprklstssd.exe O4 – HKCU\..\Run: [wdpayrmq] C:\Documents and Settings\User\Local Settings\Application Data\krtopldrf\woprklstssd.exe R1 – HKCU\Software\Microsoft\Windows\CurrentVersion\Internet Settings,ProxyServer = http=127.0.0.1:5555
The process name will be different in your case. But it has the same structure: [RANDOM]tssd.exe Select all similar entries and click once on the "Fix checked" button. Close HijackThis tool.
3. Download SUPERAntispyware, MalwareBytes Anti-malware or Spybot - Search & Destroy and run a full system scan.NOTE: before saving the selected program onto your computer, please rename the installer to winlogon.exe or iexplore.exe. Launch the program and follow the prompts. Don't forget to update the installed program before scanning.
Antivirus Suite associated files and registry values:
Files:
C:\Documents and Settings\[UserName]\Local Settings\Application Data\[random]\
C:\Documents and Settings\[UserName]\Local Settings\Application Data\[random]\[random]tssd.exe
By default "Application Data" folder is hidden. To unhide this folder (and others), open the Folder Options in the Control Panel, and on the “View” tab, change the option to “show hidden files and folders”, and click ok.