Wednesday, February 17, 2010

How to remove Personal Anti Malware fake antivirus program? (Uninstall guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Personal Anti Malware is a fake program that reports false threats and uses aggressive advertising to scare you and to trick you into thinking that your computer is infected with malware. This rogue security software claims to remove the infections in exchange of payment. Don't purchase it. Personal Anti-Malware is a scam. By the way, if you unadvisedly purchased it, contact your credit card company and dispute the charges. Another interesting thing is that if you did purchase it then you probably see a new version of the PersonalAntiMalware virus with new graphical user interface and title - Personal Anti Malware Center. One way or another, this program should be removed from the system as soon as possible. The good new is that it can be removed for free with legitimate anti-malware/spyware software. Read removal instructions below to find out how to remove Personal Anti Malware for free.


Personal Anti Malware video:


As a typical rogue program, Personal Anti-Malware displays fake warnings and pop-ups and it has its own Anti Malware Security Center called Security Essentials. Yep, you're right, just like the false scan results, these alerts and pop-ups were made to scare you and to convince you into paying for this needless software. This fake program constantly displays notification from Windows task bar with random infections:

Critical System Warning!
Your system is infected with version of [virus name].
This malicious program is a [virus type].
It infected [file name].
This [virus type] attempts to steal and corrupt your private information.
Click here to save your private information!


As you can see, Personal Anti Malware is a total scam. Don't install it and most importantly, don't purchase it. OK, let's get on with the business of disinfecting your computer. There are several free and effective removal tools that should be able to get rid of this fake program. These programs are listed in the removal guide below. It might be that you will have to use two programs to remove this infection completely. You may use more than one spyware removal software. They are all free. Also note, if you can't do anything in Normal Mode then you should reboot your PC in Safe Mode with Networking and complete the removal steps again. What is more, Personal Anti Malware may come bundled with other malicious software that is not included in the removal guide. Because of that manual Personal AntiMalware removal is not recommended.


Personal Anti Malware removal instructions (method #1):

NOTE: complete steps 1 and 2 if you can't use Internet or download/install malware removal tools listed in step 3.


1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro).
Launch the iexplore.exe and click "Do a system scan only" button.
If you can't open iexplore.exe file then download explorer.scr and run it.

2. Search for such entries in the scan results:
O4 - HKCU\..\Run: [Personal Anti Malware] C:\Program Files\Personal Anti Malware\PAM.exe
O4 - HKCU\..\Run: [Windows applications server] C:\Program Files\Personal Anti Malware\SysShield.exe
O4 - HKCU\..\RunOnce: [%Temp%\delInstav2009.bat] %Temp%\delInstav2009.bat
Select all such entries and click once on the "Fix checked" button. Close HijackThis tool.


3. Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.
NOTE1: if you can't run any of the above programs you must rename the installer of selected program before saving it on your PC. For example: if you choose MalwareBytes then you have to rename mbam-setup.exe to iexplore.exe, explorer.exe or any random name like test123.exe before saving it.

NOTE2: if you still can't run the renamed file then you need to change file extension too not only the name.
1. Go to "My Computer".
2. Select "Tools" from menu and click "Folder Options".
3. Select "View" tab and uncheck the checkbox labeled "Hide file extensions for known file types". Click OK.
4. Rename mbam-setup.exe to either test123.com or test123.pif
5. Double-click to run renamed file.


Removing Personal Anti Malware in Safe Mode with Networking (method #2):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm
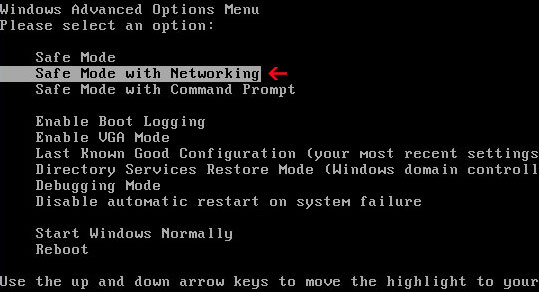


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
If you can't reboot your PC in Safe Mode with Networking, download SafeBootKeyRepair and run it. If the rogue program blocks it then download and run this file RenamedSBKRepair. Follow the prompts. Then reboot your PC in Safe Mode with Networking.

2.Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.


Personal Anti Malware files and registry values:

Files and folder:
  • C:\Documents and Settings\All Users\Start Menu\Personal Anti Malware
  • C:\Program Files\Personal Anti Malware
  • C:\Program Files\Personal Anti Malware\add.exe
  • C:\Program Files\Personal Anti Malware\AVP_Update.exe
  • C:\Program Files\Personal Anti Malware\PAM.exe
  • C:\Program Files\Personal Anti Malware\scanopt.sys
  • C:\Program Files\Personal Anti Malware\Support.url
  • C:\Program Files\Personal Anti Malware\svo.scf
  • C:\Program Files\Personal Anti Malware\sysdata.sys
  • C:\Program Files\Personal Anti Malware\SysShield.exe
  • C:\Program Files\Personal Anti Malware\Uninstall.exe
  • C:\Program Files\Personal Anti Malware\warning.mht
Registry keys and values:
  • HKEY_CURRENT_USER\Software\AV2009
  • HKEY_CURRENT_USER\Software\AVP09
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "Personal Anti Malware"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "Windows applications server"
  • HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Internet Settings\User Agent\Post Platform "AVP09"

Share this information with other people:

Monday, February 15, 2010

How to remove Security Essentials 2010 fake antivirus program? (Uninstall guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Security Essentials 2010 is a fake (rogue) antivirus program. It's a clone of Internet Security 2010. The same GUI only the name is different. Most importantly, don't confuse this rogue program with Microsoft Security Essentials which is perfectly legitimate software from reputable company. Name can be deceiving! This fake program is very irritating and if you are reading this article then you are probably infected with this scareware. Thankfully we've got several useful removal tips to help you remove Security Essentials 2010 for free.


This fake program is usually installed through the use of Trojans or other malicious software. It can be promoted via fake online scanners, misleading websites and even using social engineering methods. Once active, SecurityEssentials2010 loads many fake security warnings and popups claiming that your computer is badly infected, even though it's the only virus on your computer. The rogue program runs a fake system scan and reports false infections to scare you even more. Just like the fake security alerts, false computer threats should be ignore. Security Essentials 2010 is one of many fake antivirus applications that use various misleading methods to trick you into purchase the program. Don't do this! Instead, you should get rid of this annoying software as soon as possible.

Another very irritating thing is that Security Essentials 2010 blocks almost all programs on your computer and I'm not even talking about antivirus software. Usually, it displays an error message with the following text:

"Application cannot be executed. The file is infected. Please activate your antivirus software."

"ERROR
Application Error.The instruction at 0x009a6f9a referenced memory at 0x00000000. The memory could not be written.Click on OK to terminate the program."


"Critical Warning!
Critical System Warning! Your system is probably infected with a version of Trojan-Spy.HTML.Visafraud.a. This may result in website access passwords being stolen from Interner Explorer, Mozilla Firefox, Outlook etc. Click Yes to scan and remove threats. (recommended)"

It will also hijack your Desktop and change your default background to something like this:


As you can see, Security Essentials 2010 is a total scam. Don't pay for it! If you bought this malware, then contact your credit card company and dispute the charges. Next, read the removal guide below and remove Security Essentials 2010 from your PC for free one and for all. Good luck! By the way, if you have any questions, don't hesitate and ask.


Security Essentials 2010 removal instructions (method #1):

NOTE: complete steps 1-3 if you can't use Internet or download/install malware removal tools listed in step 4.


1. Download iexplore.exe (NOTE: iexplore.exe file is renamed HijackThis tool from TrendMicro).
Launch the iexplore.exe and click "Do a system scan only" button.
If you can't open iexplore.exe file then download explorer.scr and run it.

2. Search for such entries in the scan results:
F2 – REG:system.ini: UserInit=C:\WINDOWS\system32\winlogon32.exe
O4 – HKLM\..\Run: [smss32.exe] C:\WINDOWS\system32\smss32.exe
O4 – HKCU\..\Run: [smss32.exe] C:\WINDOWS\system32\smss32.exe
O4 – HKCU\..\Run: [Security essentials 2010] C:\Program Files\Securityessentials2010\SE2010.exe
Select all such entries and click once on the "Fix checked" button. Close HijackThis tool.


3. Download the file LSPFix.zip and extract it into a folder on your PC.
Launch LSPFix. Place a tick in the "I know what I'm doing".
In the KEEP box select helper32.dll (or randomly named file such as lsawpeajpg.dll) and press ">>" button.
Press Finish>> button. Wait while LSPFix removes helper32.dll and displays a summary. Press OK.


4. Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.
NOTE1: if you can't run any of the above programs you must rename the installer of selected program before saving it on your PC. For example: if you choose MalwareBytes then you have to rename mbam-setup.exe to iexplore.exe, explorer.exe or any random name like test123.exe before saving it.

NOTE2: if you still can't run the renamed file then you need to change file extension too not only the name.
1. Go to "My Computer".
2. Select "Tools" from menu and click "Folder Options".
3. Select "View" tab and uncheck the checkbox labeled "Hide file extensions for known file types". Click OK.
4. Rename mbam-setup.exe to either test123.com or test123.pif
5. Double-click to run renamed file.


Removing Security Essentials 2010 in Safe Mode with Networking (method #2):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
If you can't reboot your PC in Safe Mode with Networking, download SafeBootKeyRepair and run it. If the rogue program blocks it then download and run this file RenamedSBKRepair. Follow the prompts. Then reboot your PC in Safe Mode with Networking.

2.Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.


Security Essentials 2010 files and registry values:

Files:
  • C:\WINDOWS\system32\warnings.html
  • C:\WINDOWS\system32\helpers32.dll
  • C:\WINDOWS\system32\winlogon32.exe
  • C:\WINDOWS\system32\smss32.exe
  • C:\WINDOWS\system32\41.exe
  • %Temp%\250904.exe
  • %StartMenu%\Security essentials 2010.lnk
  • %Desktop%\Security essentials 2010.lnk
  • C:\ProgramFiles\Securityessentials2010\SE2010.exe
Registry keys and values:
  • HKEY_CURRENT_USER\Software\SE2010
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run
  • "Security essentials 2010"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "smss32.exe"

Share this information with other people:

Saturday, February 13, 2010

How to remove My Security Wall fake antivirus program? (Uninstall guide)

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
My Security Wall is a fake anti-virus program. It's a clone of Security Antivirus which is of course fake software too. If you are reading this article then your computer is probably infected with MySecurityWall virus. So, what does this fake program do and how to remove it? In short, My Security Wall is classified as a rogue security application because it reports false scan results, displays fake warnings, hijacks web browser and disables particular system tools (Task Manager, Regedit and etc.).

It uses these methods in order to scare you and make you think that your computer is infected with Trojans, worms and other viruses when in reality the only infection is the MySecurity Wall itself. The fake program asks to pay for a full version of the program to remove the treats and to protect your computer. That's clearly a scam. Don't purchase this bogus software and remove My Security Wall from your as soon as possible. Please read further to find out how to remove this fake software for free.


My Security Wall video: (thanks to rogueamp)


The rogue program is promoted through the use of malicious software (usually Trojans). Trojans come from fake online "My Computer" scanners, misleading videos websites. My Security Wall is also promoted using social engineering. You shouldn't click on any links that you receive from people you don't know on Facebook, MySpace and similar sites. Once installed, this fake program creates numerous fake and harmless files on your computer, just like Security Antivirus malware does. Both fake programs drop the same files in UserProfile%\Recent\ directory: ANTIGEN.exe, cid.dll, PE.drv, ANTIGEN.drv, DBOLE.sys, CLSV.drv, ddv.dll, FS.drv, ddv.sys, energy.tmp, gid.drv, PE.exe, PE.sys, PE.tmp, tjd.drv, ANTIGEN.drv, runddlkey.dll std.exe.

Furthermore, MySecurityWall displays fake warnings and pop ups claiming that your computer is infected. Fake alerts state:

"System alert!
malicious applications, which may contains Trojans, were found
on your computer and are to be removed immediately. Click
here to remove these potentially harmful items using My
Security Wall"


"Suspicious software which may be malicious has been detected on your PC. Click here to remove this threat immediately using My Security Wall.
Click here to remove all potentially harmful programs found immediately using My Security Wall."


The biggest problem is that this virus blocks legitimate anti-virus and anti-spyware programs. It also disables Task Manager and other useful Windows system tools. Last, but not least, it modifies Windows Hosts file and adds many malicious lines. Because of that you will be constantly redirected to various bogus websites full of ads and false information or even porn sites. Search results will be probably redirected to findgala.com. As you can see, My SecurityWall is a total scam and serious threat. Get rid of it immediately. If you have purchased it, then you should contact your credit card company as soon as possible and dispute the charges. Read My Security Wall removal instructions below. Good luck and be safe!


My Security Wall removal instructions (method #1):

Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.
NOTE1: if you can't run any of the above programs you must rename the installer of selected program before saving it on your PC. For example: if you choose MalwareBytes then you have to rename mbam-setup.exe to iexplore.exe, explorer.exe or any random name like test123.exe before saving it.

NOTE2: if you still can't run the renamed file then you need to change file extension too not only the name.
1. Go to "My Computer".
2. Select "Tools" from menu and click "Folder Options".
3. Select "View" tab and uncheck the checkbox labeled "Hide file extensions for known file types". Click OK.
4. Rename mbam-setup.exe to either test123.com or test123.pif
5. Double-click to run renamed file.


Removing My Security Wall in Safe Mode with Networking (method #2):

1. Reboot your computer is "Safe Mode with Networking". As the computer is booting tap the "F8 key" continuously which should bring up the "Windows Advanced Options Menu" as shown below. Use your arrow keys to move to "Safe Mode with Networking" and press Enter key. Read more detailed instructions here: http://www.computerhope.com/issues/chsafe.htm


NOTE: Login as the same user you were previously logged in with in the normal Windows mode.
If you can't reboot your PC in Safe Mode with Networking, download SafeBootKeyRepair and run it. If the rogue program blocks it then download and run this file RenamedSBKRepair. Follow the prompts. Then reboot your PC in Safe Mode with Networking.

2.Download one of the following legitimate anti-malware applications and run a quick system scan. Don’t forget to update it first. All programs a free.


My Security Wall files and registry values:

Folders and files:
  • C:\Documents and settings\All Users\ Application Data\25def\
  • C:\Documents and settings\All Users\ Application Data\25def\72.mof
  • C:\Documents and settings\All Users\ Application Data\25def\mozcrt19.dll
  • C:\Documents and settings\All Users\ Application Data\25def\MA3S5f.exe
  • C:\Documents and settings\All Users\ Application Data\25def\SAV.ico
  • C:\Documents and settings\All Users\ Application Data\25def\sqlite3.dll
  • C:\Documents and Settings\All Users\Application Data\MEXCIRFZ\
  • C:\Windows\System32\MSWSys\
  • %UserProfile%\Application Data\My Security Wall
  • %UserProfile%\Recent\ANTIGEN.drv
  • %UserProfile%\Recent\ANTIGEN.exe
  • %UserProfile%\Recent\cid.dll
  • %UserProfile%\Recent\CLSV.drv
  • %UserProfile%\Recent\DBOLE.sys
  • %UserProfile%\Recent\ddv.dll
  • %UserProfile%\Recent\ddv.sys
  • %UserProfile%\Recent\energy.tmp
  • %UserProfile%\Recent\FS.drv
  • %UserProfile%\Recent\gid.drv
  • %UserProfile%\Recent\PE.drv
  • %UserProfile%\Recent\PE.exe
  • %UserProfile%\Recent\PE.sys
  • %UserProfile%\Recent\PE.tmp
  • %UserProfile%\Recent\runddlkey.dll
  • %UserProfile%\Recent\std.exe
  • %UserProfile%\Recent\tjd.drv
  • %UserProfile%\Recent\tjd.sys
  • C:\Program Files\Mozilla Firefox\searchplugins\search.xml
Registry values:
  • HKEY_USERS\.DEFAULT\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=7&q={searchTerms}"
  • HKEY_CURRENT_USER\Software\Classes\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=7&q={searchTerms}"
  • HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Download "RunInvalidSignatures" = "1"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Internet Settings\5.0\User Agent\Post Platform "Build/13.00007"
  • HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Run "My Security Wall"
  • HKEY_CLASSES_ROOT\Software\Microsoft\Internet Explorer\SearchScopes "URL" = "http://findgala.com/?&uid=7&q={searchTerms}"
  • HKEY_CLASSES_ROOT\xp_5f014.DocHostUIHandler

Share this information with other people:

Securityessentials2010.com and other misleading sites. Looks can be deceiving!

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
Yesterday I read Paretologic.com blog entry about scam using Security Essentials. Jerome Segura mentioned essentials2010.org and he was right, you should avoid it - total scam. Cyber criminals ask to pay for Microsoft Security Essentials. As you know, this product is free and can be downloaded from official website without any subscriptions and etc. I came across another eight sites (there are probably more) that are similar to essentials2010.org.
  • securityessentials2010.com
  • securityessentials-2010.com
  • essentialsfree.info
  • essentialsfree.net
  • essentialsfree.org
  • essentials-free.org
  • essentials-pro.com
  • essentialssite.com
Here's an example of Securityessentials2010.com scam. I have to admit that the scam site looks quite professional, but as I said, looks can be deceiving! The misleading site uses MalwareBytes icon, that's very strange. There are three download buttons and they all redirect users to Freedownloadzone.com. DON'T make any payments through this site otherwise you will simple lose your money.


Share this information with other people:

Wednesday, February 10, 2010

“Warning! Spambot detected!” fake warning from Security Antivirus scareware

Don't Copy From This Blog...

Protected by Copyscape Plagiarism Detection
"Warning! Spambot detected!" is one of many fake security alerts that will popup on your screen while you are infected with the fake anti-virus program called Security Antivirus. The fake warning claims:

"Warning! Spambot detected!
Attention! A spambot sending viruses to your e-mail contacts has been detected on your PC."

The main goal of this fake message is to scare you into thinking that your computer is compromised. If you click “Yes” to this warning then you will be redirected to the pay page of the bogus software Security Antivirus. Don’t be fooled and remove the rogue program from your computer immediately. Please read the Security Antivirus removal instructions to find out how to remove this virus for free.

 
//PART 2